mirror of
https://github.com/paperclipai/paperclip.git
synced 2026-11-04 11:01:16 +01:00
377ebefd03c65518c254c4d4140c4ac2ff379d15
2922
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 Dotta |
377ebefd03 |
Merge secrets unified UX + table redesign chain (PAP-12267 branch tip 84507ce60) into PAP-12349 branch off current master
Co-Authored-By: Paperclip <noreply@paperclip.ing> # Conflicts: # packages/db/src/migrations/meta/_journal.json |
||
|
Dotta
|
84507ce609 | Fix secrets responsive table breakpoint | ||
|
DottaandPaperclip
|
f5d7a13aba |
Fix secrets dialog provider fallback loop
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
Dotta
|
8e7ac6c69e | Redesign secrets table and drawer | ||
|
scotttongandClaude Opus 4.8
|
fb2b760915 |
fix(issues): attribute agent-authored comments instead of rendering them as "Board" (#8833)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work
> - Task/issue threads render each comment as a chat bubble; the author
determines whether it shows as a left-aligned agent bubble (name + icon)
or a right-aligned "Board" bubble
> - Comments posted by an agent from a local execution environment are
written with a non-human author id (`local-board`/system), so they were
mis-rendered as blue "Board" bubbles instead of being attributed to the
authoring agent
> - This misattribution is confusing (it looks like the human board said
something an agent actually said) and it can drive false
wake/reconciliation behavior on the affected threads
> - This pull request adds server-side attribution derivation (lossless
run-id join first, then an explicit run-log post marker), persists the
derived agent so the read path stops re-scanning run logs, and stops the
client from labeling agent-derived comments "Board"
> - The benefit is agent comments render as the correct agent, genuine
human board comments are never reattributed, and reads get cheaper after
a one-time persistence

## Linked Issues or Issue Description

<!-- No public GitHub issue — describing the problem in-PR (bug report
shape). -->

**What happened?**

In a task/issue comment thread, comments authored by an agent from a
local execution environment are stored with a non-human author id
(`local-board`/system). The UI renders these as right-aligned blue
"Board" bubbles, implying a human board member authored them. The
mislabeling is also a wake/reconciliation hazard: an agent comment that
reads as "Board" can look like human board input.

**Expected behavior**

Such comments should render as the authoring agent (left-aligned bubble
with agent name + icon). Genuine human/board comments must continue to
render as "Board" and must never be reattributed to an agent.

**Steps to reproduce**

1. Have an agent post a comment on an issue from a local execution
environment (author id `local-board`).
2. Open the issue comment thread in the UI.
3. Observe the agent's comment rendered as a right-aligned blue "Board"
bubble instead of the authoring agent.

**Root cause**

The read path did not resolve the authoring agent for these comments,
and the client fell back to a "Board" label for the `local-board`
author.

## What Changed

- **Server derivation (`server/src/services/issues.ts`):**
- Resolve the authoring agent from the comment's run id first
(`createdByRunId`/`derivedCreatedByRunId` → `heartbeatRuns.agentId`) —
lossless when present.
- Second tier `run_log_comment_post`: read the run log lazily (only for
still-unresolved comments) to match the explicit `comment id:` post
marker.
- **Guard:** never reattribute a comment whose author maps to a genuine
user profile. Only the non-human sentinel (`local-board`, which is
itself a `user` row) and authors absent from the `user` table are
eligible.
- Pure timing-overlap tiers are intentionally **not** used (Option A) —
an agent comment and a human board comment posted during the same run
are indistinguishable rows, so any timing guess risks mislabeling a real
human comment.
- **Persistence
(`packages/db/src/migrations/0126_issue_comment_derived_attribution.sql`,
`packages/db/src/schema/issue_comments.ts`):** add stored `derived_*`
attribution columns and write the resolved agent back with a single bulk
`UPDATE ... FROM (VALUES ...)`, so reads stop recomputing from run logs.
Migration is additive (new nullable columns) with a batched, idempotent
backfill of the lossless run-id tier over historical rows.
- **Types (`packages/shared/src/types/issue.ts`):** expose the persisted
attribution fields and the `IssueCommentDerivedAuthorSource` union.
- **Client (`ui/src/lib/issue-chat-messages.test.ts`):** the message
builder already prefers a resolved agent id (`authorAgentId ??
runAgentId ?? derivedAuthorAgentId`), so once the server persists the
derived agent the bubble renders as the agent automatically — no client
code change needed. Adds a regression guard confirming a genuine board
comment with no derived agent is still rendered as "Board".
- **Tests:** derivation + message-building tests, including assertions
that genuine board/user comments are **not** reattributed.

## Verification

- `cd server && npx vitest run issues-service` — 94 tests pass: run-id
resolution, no-attribution on timing overlap alone (Option A), multi-run
ambiguity, same-agent multi-run, and the genuine-user guard. Exercises
the real persistence path (bulk UPDATE) against the test DB.
- `cd ui && npx vitest run issue-chat-messages` — 27 tests pass; client
no longer labels agent-derived comments "Board", and a genuine board
comment with no derived agent is not re-labeled.
- `cd server && npm run typecheck` — passes (exit 0).
- Manual: on a thread containing old agent-authored comments, the blue
"Board" bubbles render as the authoring agent; a genuine board comment
on the same thread still renders as "Board".

## Risks

- **Mis-reattributing a genuine board comment made during an agent run**
→ mitigated by the human-profile guard (only `local-board`/system
authors are eligible) and by dropping pure timing tiers (Option A): only
the lossless run-id join and the explicit run-log post marker attribute
history.
- **Backfill volume / run-log reads** → the migration backfill is
batched (5000 rows/loop) and results are persisted so reads stop
recomputing; the read-path persistence is a single bulk UPDATE rather
than per-comment round-trips. Migration adds only nullable columns (no
destructive change).
- The persistence/backfill has **not** been run against any production
database as part of opening this PR.

## Model Used

Claude Opus 4.8 (`claude-opus-4-8`), extended thinking, via Claude Code
with tool use.

## Checklist

- [x] I have included a thinking path that traces from project context
to this change
- [x] I have specified the model used (with version and capability
details)
- [x] I have checked ROADMAP.md and confirmed this PR does not duplicate
planned core work
- [x] I have searched GitHub for duplicate or related PRs — related open
PRs (#6006 narrow attribution run scan, #4729 attribution roll-up, #7014
reaped-run attribution) address different attribution paths; none fix
the `local-board` "Board" bubble rendering this PR targets. Supersedes
#8832 (same change; branch renamed to drop an internal ticket id per
CONTRIBUTING → Branch Naming)
- [x] I have either (a) linked existing issues with `Fixes: #` / `Closes
#` / `Refs #` OR (b) described the issue in-PR following the relevant
issue template
- [x] I have not referenced internal/instance-local Paperclip issues or
links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip`
URLs)
- [x] My branch name describes the change and contains no internal
Paperclip ticket id or instance-derived details
- [x] I have run tests locally and they pass
- [x] I have added or updated tests where applicable
- [x] I have updated relevant documentation to reflect my changes
- [x] I have considered and documented any risks above
- [x] All Paperclip CI gates are green
- [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups
- [x] I will address all Greptile and reviewer comments before
requesting merge

Co-authored-by: Claude Opus 4.8 <noreply@anthropic.com>
canary/v2026.702.0-canary.0 |
||
|
DottaandPaperclip
|
e38f34ef69 |
Fix secrets create provider selection
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
0ac5ac5467 |
Unify secrets admin UX
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
c61055bbec |
fix(secrets): ignore null user-secret patch selectors
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
b58da3f674 |
fix(secrets): ignore null user-secret patch values
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
f3727a6fb0 |
fix(secrets): require explicit responsible users
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
7c7f9b1767 |
fix(secrets): close user definition edge cases
Reject deleted status during user-secret definition creation and remove the stale key field from the UI update contract. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
Evyatar BluzerandAndrew Aymeloglu
|
de837e2683 |
refactor(a11y): issues view toggle aria attributes and goal tree expand buttons (#1939)
## Thinking Path

Two interactive UI controls were missing WAI-ARIA attributes, so
screen-reader users couldn't perceive their state. The IssuesList
view-mode toggle already had `title` tooltips but no
`aria-label`/`aria-pressed` and its container had no `role="group"`; the
GoalTree expand/collapse chevron announced only "button". Approach:
attributes only, no logic/render changes, reusing the pattern already
shipped on the Agents page toggle. Per review feedback, GoalTree uses a
**stable** `aria-label` (`` `${goal.title} subtree` ``) with
`aria-expanded` for state, rather than a dynamic label that
double-announces state.

## Issue

_No existing tracking issue — described inline per CONTRIBUTING.md →
"Link Issues or Describe Them In-PR"._

**What happened**
Two components expose buttons with no accessible name or state, making
them unusable via screen reader: (1) the `IssuesList` view-mode toggle
doesn't convey which view is active; (2) the `GoalTree` expand/collapse
chevrons have no name and no expanded/collapsed state.

**Expected behavior**
Both controls announce their purpose and current state to assistive
technology.

**Steps to reproduce**
Enable VoiceOver, open the Issues page and Tab to the view-mode toggle,
then open the Goals page with nested goals and Tab to a tree chevron —
each control announces only "button", with no name and no
pressed/expanded state.

## What Changed

**`ui/src/components/IssuesList.tsx`** — `role="group"` +
`aria-label="View mode"` on the container; `aria-label` ("List
view"/"Board view") and `aria-pressed` on each button.

**`ui/src/components/GoalTree.tsx`** — stable `aria-label` (``
`${goal.title} subtree` ``) and `aria-expanded` on the chevron button.

2 files, ARIA attributes only, no behavioral change.

## Verification

1. Issues page → toggle announces "List view, pressed" / "Board view,
not pressed", grouped as "View mode".
2. Goals page with nested goals → each chevron announces "<goal title>
subtree" with expanded/collapsed state.
3. Manual VoiceOver pass; no visual/behavioral change for sighted users.

## Risks

Minimal — additive HTML attributes with no impact on logic, rendering,
or state. Worst case is a suboptimal announcement string, trivially
adjusted.

## Model Used

Original change human-authored by @bluzername. Two follow-up commits
(stable `aria-label` refinement; removal of a stray tooling file)
applied via maintainer edit; the refinement was drafted with Claude Opus
4.8.

## Checklist

- [x] I searched the GitHub PR list (open + recently closed) for
similar/duplicate PRs before opening — none found.

---------

Co-authored-by: Andrew Aymeloglu <aaymeloglu@gmail.com>
canary/v2026.701.0-canary.5
|
||
|
DottaandPaperclip
|
8da5a0b44a |
fix(secrets): skip deleted optional user secrets
Let optional user-secret bindings resolve to null when their definition has been deleted, matching the pre-dispatch gate's optional-binding behavior. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
b04069d14d |
fix(secrets): preserve external rotation selectors
Reject empty rotation requests while still allowing external-reference rotations that intentionally supply only provider version or provider config selectors. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
7a5738b6dc |
fix(secrets): validate user-secret rotations
Require rotation payloads to include literal material or an external reference, apply the stricter schema to current-user secret rotation routes and OpenAPI, and let optional user-secret bindings quietly omit disabled definitions during runtime resolution. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
Nicky LeachandPaperclip
|
3522b1c9be |
Emit interaction resolved telemetry (#8824)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work
> - Issue-thread interactions are how agents ask users or the board for
decisions and structured input
> - Product telemetry needs to understand when those interactions
resolve without exposing private interaction content
> - Resolution currently happens through several service paths, so
telemetry needs to be emitted consistently from the terminal transitions
> - The interaction service should describe the resolved interaction,
while the telemetry backend owns unknown-value normalization for
dimensions
> - This pull request emits `interaction.resolved` after successful
database writes and removes redundant client-side normalization from the
service
> - The benefit is aggregate-safe telemetry for interaction completion
behavior without leaking raw IDs, answer text, rejection reasons, or
document content

## Linked Issues or Issue Description

No public GitHub issue exists for this internal telemetry follow-up.

Feature context:

- Problem/motivation: Paperclip needs aggregate product telemetry for
issue-thread interaction resolution outcomes while preserving privacy
boundaries around user answers and internal identifiers.
- Proposed solution: Emit `interaction.resolved` once from terminal
interaction resolution paths, passing runtime dimensions through the
shared telemetry helper while preserving aggregate-safe counts and
ID/free-text omission.
- Alternatives considered: Normalizing interaction dimensions in the
interaction service duplicated telemetry backend responsibility and made
unknown-value handling inconsistent across telemetry clients.
- Roadmap alignment: This is a focused telemetry instrumentation
follow-up that builds on the generated telemetry event types from #8818.

## What Changed

- Wires `interaction.resolved` telemetry into terminal issue-thread
interaction resolution paths after successful database writes.
- Passes raw interaction kind, status, continuation policy, resolution
reason, target type, and creator agent role values to the shared
telemetry helper instead of maintaining service-local allowlists.
- Preserves resolver classification, target `none` derivation for
non-confirmation interactions, non-negative aggregate counts, raw ID
omission, and free-text omission.
- Logs telemetry failures without blocking interaction resolution.
- Adds service-level tests for accepted, rejected, answered,
stale-target expiry, superseded-comment expiry, and raw creator-role
pass-through payloads.

## Verification

- `pnpm run preflight:workspace-links && pnpm exec vitest run
server/src/__tests__/issue-thread-interactions-telemetry.test.ts
server/src/__tests__/shared-telemetry-events.test.ts`
- `pnpm typecheck`
- GitHub PR checks on the latest head commit are green, including
`verify`, build, e2e, general tests, serialized server suites, security
scans, and Greptile Review.
- Security code review completed before this branch update.

## Risks

- Low operational risk: telemetry is emitted after successful
persistence and telemetry failures are logged without blocking the
user-visible interaction flow.
- Main behavioral risk is duplicate or missing telemetry from a
resolution path; the focused tests cover the terminal resolution
variants.
- Telemetry dimension normalization now depends on the shared telemetry
backend path instead of the interaction service, so backend
normalization must remain the source of truth for unknown or empty
dimension values.
- The existing PR branch name contains an internal task id because this
update continues an already-open PR branch instead of opening a
replacement PR.

## Model Used

OpenAI GPT-5 Codex coding agent, API-based coding environment with
shell, repository, and GitHub CLI tool use. Context window size was not
reported by the runtime.

## Checklist

- [x] I have included a thinking path that traces from project context
to this change
- [x] I have specified the model used (with version and capability
details)
- [x] I have checked ROADMAP.md and confirmed this PR does not duplicate
planned core work
- [x] I have searched GitHub for duplicate or related PRs and linked
them above
- [x] I have either (a) linked existing issues with `Fixes: #` / `Closes
#` / `Refs #` OR (b) described the issue in-PR following the relevant
issue template
- [x] I have not referenced internal/instance-local Paperclip issues or
links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip`
URLs)
- [ ] My branch name describes the change (e.g. `docs/...`, `fix/...`)
and contains no internal Paperclip ticket id or instance-derived details
- [x] I have run tests locally and they pass
- [x] I have added or updated tests where applicable
- [x] I have updated relevant documentation to reflect my changes
- [x] I have considered and documented any risks above
- [x] All Paperclip CI gates are green
- [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups
- [x] I will address all Greptile and reviewer comments before
requesting merge

---------

Co-authored-by: Paperclip <noreply@paperclip.ing>
canary/v2026.701.0-canary.4 |
||
|
DottaandPaperclip
|
beb9d77ec8 |
test(server): make file resource prefixes deterministic
Avoid random issue-prefix collisions in the file resource test graph seed helper. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
|
d68c34f2cc |
Fix managed workspace branch coherence recovery (#8826)
## Thinking Path > - Paperclip is the open source app people use to manage AI agents for work. > - Managed issue workspaces are part of the control-plane runtime boundary: the server records which git worktree and branch an agent run is allowed to use. > - Existing reuse checks validated the worktree path and cleanliness, but did not fully validate that the actual checked-out branch still matched the recorded execution workspace branch. > - That gap let an agent run switch a managed worktree onto a publishing branch without updating the execution workspace record, then later reuse or finalize the workspace as though it were coherent. > - The runtime needs a bounded repair path for provably safe mismatches and a hard validation failure for dirty, divergent, or unrecorded branch transitions. > - This pull request adds branch coherence to managed git worktree validation, records explicit recovery evidence, and prevents finalize success when a run silently changes branches. > - The benefit is that branch drift becomes either safely repaired or visibly recoverable instead of silently corrupting managed workspace state. ## Linked Issues or Issue Description No public GitHub issue exists for this bug. Bug report: - What happened: a managed agent workspace could be recorded for one branch while the underlying git worktree was actually checked out on another branch. Reuse and finalization could still treat the workspace as healthy. - Expected behavior: managed git worktrees should verify the actual branch against the recorded execution workspace branch. Safe same-HEAD clean mismatches may be repaired, while dirty, divergent, or unrecorded branch transitions should fail into explicit workspace validation recovery. - Reproduction outline: create a runtime-managed issue worktree, switch its checkout to another branch without updating the execution workspace record, then attempt reuse or run finalization. - Deployment mode: local/self-hosted Paperclip server using managed git workspaces. - Related public work: Refs #7644 and #7579. Related but not duplicate: #8275 and #5851. ## What Changed - Added managed git worktree branch inspection, formatted validation evidence, and safe same-HEAD repair logic to the workspace runtime service. - Validated recorded managed workspace branch state before reuse and during heartbeat setup. - Added finalization-time branch guards so runs that silently switch branches fail with `workspace_validation_failed` instead of recording a successful finalize. - Added recovery fingerprints and evidence for `git_worktree_branch_incoherence`, including manual-repair next actions for unsafe branch drift. - Documented branch coherence as part of runtime-created git worktree workspace coherence. - Added focused tests for safe branch repair, dirty/divergent recovery evidence, heartbeat setup validation, and finalize failure/success paths. ## Verification - `pnpm install --frozen-lockfile` - `git diff --check origin/master...HEAD` - `pnpm exec vitest run server/src/__tests__/workspace-runtime.test.ts server/src/__tests__/heartbeat-workspace-session.test.ts server/src/__tests__/issue-recovery-actions.test.ts server/src/__tests__/heartbeat-workspace-finalize-branch.test.ts` - `pnpm -r typecheck` - `pnpm test:run` - `pnpm build` Notes: - An initial full `pnpm test:run` attempt hit a transient `socket hang up` in one `plugin-routes-authz` case. The exact case passed when rerun directly, the full `plugin-routes-authz` file passed, and the subsequent full `pnpm test:run` passed. - `pnpm build` still emits existing Vite CSS pseudo-element and chunk-size warnings unrelated to this change. ## Risks - This intentionally changes behavior for managed runs that switch branches without recording the transition: they now fail during workspace validation/finalization instead of silently proceeding. - The automatic repair path is intentionally narrow. It only repairs clean branch mismatches when both branches point at the same commit; dirty or divergent worktrees require manual recovery. - Recovery fingerprints now include workspace-validation evidence, so duplicate recovery-action grouping is more precise for branch-incoherence failures. > For core feature work, check [`ROADMAP.md`](ROADMAP.md) first and discuss it in `#dev` before opening the PR. Feature PRs that overlap with planned core work may need to be redirected — check the roadmap first. See `CONTRIBUTING.md`. ## Model Used OpenAI Codex, GPT-5 Codex CLI/API coding agent, with shell/git/test execution and reasoning mode enabled. ## Checklist - [x] I have included a thinking path that traces from project context to this change - [x] I have specified the model used (with version and capability details) - [x] I have checked ROADMAP.md and confirmed this PR does not duplicate planned core work - [x] I have searched GitHub for duplicate or related PRs and linked them above - [x] I have either (a) linked existing issues with `Fixes: #` / `Closes #` / `Refs #` OR (b) described the issue in-PR following the relevant issue template - [x] I have not referenced internal/instance-local Paperclip issues or links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip` URLs) - [x] My branch name describes the change (e.g. `docs/...`, `fix/...`) and contains no internal Paperclip ticket id or instance-derived details - [x] I have run tests locally and they pass - [x] I have added or updated tests where applicable - [x] I have updated relevant documentation to reflect my changes - [x] I have considered and documented any risks above - [ ] All Paperclip CI gates are green - [ ] Greptile is 5/5 with no open P2s, recommendations, or follow-ups - [x] I will address all Greptile and reviewer comments before requesting merge --------- Co-authored-by: Cody <noreply@paperclip.ing> Co-authored-by: Cody <cody@paperclip.ing> |
||
|
DottaandPaperclip
|
259b9a665a |
fix(secrets): harden user-secret review gaps
Cover adapter-config user_secret_ref entries in the pre-dispatch missing-secret gate, prevent user-secret definition key renames through the update validator, and stop the UI from sending immutable keys on definition edits. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
Evyatar Bluzer
|
be8ae528c4 |
fix(a11y): add aria-pressed to date preset and day-of-week toggle buttons (#1913)
## Thinking Path

> - Paperclip orchestrates ai-agents for zero-human companies
> - But humans want to watch the agents and oversee their work
> - Human users interact with the dashboard UI to monitor costs,
schedules, and agent behavior
> - The UI has toggle button groups where you click one option and other
become unselected (like date range presets, day-of-week selectors)
> - Visually the active button look different (filled vs outlined), but
screen reader users hear no difference - all buttons sound same
> - The `aria-pressed` attribute is what screen readers need to announce
which toggle is active and which is not
> - I searched entire UI codebase for `aria-pressed` and found zero
usage anywhere
> - This pull request adds `aria-pressed={isActive}` to two toggle
button groups: date range presets in Costs page and day-of-week selector
in ScheduleEditor
> - Now screen reader users can tell which button is currently selected
without relying on visual styling only

## Problem

The app has button groups that work like toggles - you click one button
to select it and the others become unselected. Visually this work fine
because the active button change to a different variant (filled vs
outlined). But for screen reader users, ALL buttons sound exactly the
same - just "button, 7 days", "button, 30 days", etc with no way to tell
which one is currently active.

I searched the entire UI codebase for `aria-pressed` and found zero
results. This attribute is what screen readers need to announce "7 days,
pressed" vs "30 days, not pressed" for toggle button groups.

## What I changed

Added `aria-pressed={isActive}` to two toggle button groups:

1. **Costs.tsx** - Date range preset buttons (7d, 30d, 90d, Custom).
Screen reader now announce which date range is selected.

2. **ScheduleEditor.tsx** - Day of week selector (Mon, Tue, Wed...).
Screen reader now announce which day is selected for weekly schedule.

## How to test

1. Go to Costs page, use VoiceOver (Cmd+F5 on Mac)
2. Tab through the date preset buttons
3. Active button should announce "pressed", others "not pressed"
4. Same for ScheduleEditor - create/edit trigger with weekly preset, tab
through day buttons

2 files, 2 lines added.
canary/v2026.701.0-canary.3
|
||
|
DottaandPaperclip
|
bc305047d7 |
docs(api): document user-secret routes
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
fbdb4ad94d |
test: align fixtures with user-secret contracts
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
1a0c7bee75 |
Enforce low-trust allowlist for user secrets
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
4fb2d46cb5 |
Wrap My-secrets row header so key chip reflows on mobile
The definition name + key code chip sat in a non-wrapping flex row, so at narrow (390px) widths the key chip overflowed its column and overlapped the Update/trash action cluster. Match the admin definitions row by wrapping. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
Nicky LeachandPaperclip
|
8a93a0de4c |
Implement generated client telemetry types (#8818)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work.
> - Telemetry is part of the control plane's operational visibility and
needs stable event contracts.
> - The shared telemetry client accepted first-party event names through
a broad string surface, which weakened compile-time guarantees.
> - Plugin telemetry still needs a dynamic path because plugin-defined
events cannot be enumerated in the core generated type module.
> - This pull request vendors generated Paperclip telemetry event and
dimension types, closes the first-party event-name union, and keeps
plugin telemetry on an explicit dynamic method.
> - Review feedback clarified that backend normalization should remain
the source of truth, so telemetry helpers now preserve raw categorical
values while keeping generated per-event type hints.
> - The benefit is stricter first-party telemetry typing without hiding
backend normalization signals or changing batching, flushing, schema
versioning, sinks, or endpoints.

## Linked Issues or Issue Description

No public GitHub issue exists for this internal type-contract
maintenance change.

### Problem or motivation

The shared telemetry client should reject unregistered first-party event
names at compile time, while the plugin telemetry bridge must continue
to emit plugin-defined events through the existing batching and envelope
path. Helper wrappers should also avoid client-side enum coercion so the
backend can detect and record normalization when clients send unexpected
categorical values.

### Proposed solution

Generate and vendor the accepted Paperclip telemetry event and dimension
types, use those types for the first-party `track()` API, keep
plugin-defined telemetry on an explicit dynamic method, and let helper
wrappers pass raw categorical dimensions through to backend validation.

### Alternatives considered

Keeping `track()` open to arbitrary strings would preserve flexibility,
but it would not give first-party callers the type safety this change is
meant to provide. Enumerating plugin events in core was also ruled out
because plugin-defined events are not known to the core package.
Client-side enum normalization was removed after review because it
duplicates backend validation and can hide misbehaving-client signals.

### Roadmap alignment

This is a tightly scoped telemetry contract maintenance change and does
not overlap with a roadmap-level core feature.

## What Changed

- Vendored the generated Paperclip telemetry event and dimension type
module under shared telemetry code.
- Closed the first-party telemetry event-name union to generated
backend-accepted names plus an explicit `RegisteredPluginEventName =
never` extension point.
- Added `TelemetryClient.trackDynamic()` for plugin telemetry bridge
emission while keeping `track()` closed and typed.
- Added JSDoc explaining when to use `track()` versus `trackDynamic()`.
- Updated telemetry helper wrappers to type dimensions from each event's
generated schema entry while passing raw categorical values through for
backend normalization.
- Added `trackInteractionResolved()` and updated focused shared/server
tests for telemetry event typing, raw pass-through behavior, and plugin
telemetry bridging.

## Verification

Local verification passed before the latest push:

- `pnpm --filter @paperclipai/shared typecheck`
- `pnpm --filter @paperclipai/server typecheck`
- `pnpm exec vitest run
packages/shared/src/telemetry/client-types.test.ts
server/src/__tests__/shared-telemetry-events.test.ts
server/src/__tests__/plugin-telemetry-bridge.test.ts
server/src/__tests__/project-goal-telemetry-routes.test.ts
server/src/__tests__/routine-run-telemetry.test.ts
server/src/__tests__/issue-telemetry-routes.test.ts`
- `git diff --check`

Post-push verification completed on head
`3d973ffbea6154b19ad208dcffd1374d1b25b654`:

- GitHub PR checks passed, including `verify`, build, typecheck/release
registry, general test shards, serialized server shards, canary dry run,
e2e, and security checks.
- Greptile Review passed with 5/5 confidence.
- All PR review threads are resolved.

## Risks

Low runtime risk. The change is intended to affect TypeScript contracts
and helper typing while preserving the existing telemetry enqueue,
batching, and backend ingest path. The main intentional behavior shift
is that helper wrappers no longer coerce unexpected categorical values
on the client; those values reach the backend so backend normalization
can record the signal. Private company import source refs still use
`hashPrivateRef` when `isPrivate` is true.

## Model Used

OpenAI GPT-5 Codex, tool-enabled coding agent. Exact context window was
not exposed by the runtime; the agent used repository file access, shell
commands, and GitHub CLI operations.

## Checklist

- [x] I have included a thinking path that traces from project context
to this change
- [x] I have specified the model used (with version and capability
details)
- [x] I have checked ROADMAP.md and confirmed this PR does not duplicate
planned core work
- [x] I have searched GitHub for duplicate or related PRs and linked
them above
- [x] I have either (a) linked existing issues with `Fixes: #` / `Closes
#` / `Refs #` OR (b) described the issue in-PR following the relevant
issue template
- [x] I have not referenced internal/instance-local Paperclip issues or
links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip`
URLs)
- [x] My branch name describes the change (e.g. `docs/...`, `fix/...`)
and contains no internal Paperclip ticket id or instance-derived details
- [x] I have run tests locally and they pass
- [x] I have added or updated tests where applicable
- [x] I have updated relevant documentation to reflect my changes
- [x] I have considered and documented any risks above
- [x] All Paperclip CI gates are green
- [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups
- [x] I will address all Greptile and reviewer comments before
requesting merge

---------

Co-authored-by: Paperclip <noreply@paperclip.ing>
canary/v2026.701.0-canary.2 |
||
|
DottaandPaperclip
|
30b50c1a76 |
Add user-secret Storybook story; fix singular nudge copy
- Storybook Product/User secrets stories: admin definitions, my secrets,
  missing-secret warning, and env picker (seeded caches, no backend).
- MyUserSecretsTab: correct singular grammar ("1 required secret still
  needs your value").

Co-Authored-By: Paperclip <noreply@paperclip.ing>
|
||
|
Ege Chelebi
|
41059841f1 |
feat(gemini-local): add Gemini 3.1 Pro models to gemini-local adapter (#1602)
**Thinking path**

The gemini_local adapter's model dropdown
(packages/adapters/gemini-local/src/index.ts)
still lists only Gemini 2.x. Google has since shipped the Gemini 3.1 Pro
family, so users
can't pick the current flagship from the dashboard and instead hit
ModelNotFoundError when
they type an ID by hand (#1506). The adapter passes the selected string
straight to
`gemini --model`, so the fix is to surface the valid 3.1 Pro IDs in the
list.

**What I did**
Added two entries to the `models` array, above the existing 2.x entries:
- `gemini-3.1-pro-preview` — Gemini 3.1 Pro (Preview)
- `gemini-3.1-pro-preview-customtools` — custom-tools variant, tuned for
agentic/tool use

**Why it matters**
Users can select the current flagship 3.1 Pro (and its custom-tools
endpoint) directly,
instead of guessing IDs and hitting ModelNotFoundError.

**How to verify**
Open the gemini_local model dropdown in the dashboard; both entries
appear above the 2.5
entries and run against `gemini --model <id>` without error.

**Risks**
Minimal — additive, single-file change to a static list; nothing
removed. Both IDs are
confirmed-valid Google API identifiers.

Fixes #1506.
canary/v2026.701.0-canary.1 |
||
|
DottaandPaperclip
|
9294de6d1e |
Test user-secret UI helpers, warning banner, and env picker
- user-secret-presentation/my-value-state: coverage counts-only label, my-value state derivation, status tones. - MissingUserSecretsBanner: warns about unset active user secrets, renders nothing when satisfied or disabled, and opens the set-value dialog (the warning path AC). - EnvVarEditor: renders user_secret_ref rows with definition + Required, exposes the User secret source and Company secret rename, and preserves company-secret behavior. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
8d10c84ed2 |
Backfill test/story fixtures for user-secret contract fields
The user-specific secret contracts (
|
||
|
DottaandPaperclip
|
34076590d7 |
Add missing-user-secret warning path and access-event owner metadata
- MissingUserSecretsBanner: reusable warning listing the current user's unset user secrets with inline "Set value" (shared SetMyUserSecretDialog). Renders nothing when there is nothing missing, so it is safe to embed. Mounted on the New Issue dialog (task creation surface). - Secret access events now show the User-secret scope badge, responsible user, and credential owner (resolved via the company user directory), satisfying the user-secret owner metadata deliverable. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
a5673e8149 |
Add user-secret Secrets tabs and env binding picker
Phase 6 UI (PAP-12280) for user-specific secrets: - Secrets page: new "User secret definitions" (admin) and "My secrets" (owner) tabs; rename first tab to "Company secrets". Tabs are visually distinct via a violet accent vs company secrets' neutral/emerald. - UserSecretDefinitionsTab: create/edit/delete company definitions with coverage shown as counts only (never values). - MyUserSecretsTab + SetMyUserSecretDialog: each member sets/updates/clears their own value; dialog is shared so it can also satisfy a missing required secret from warning surfaces. - EnvVarEditor: third binding source "User secret" (user_secret_ref) with a definition picker and Required/Optional toggle; rename bare "Secret" to "Company secret". Wired user-secret definitions into agent and project env. - api/secrets + queryKeys: user-secret-definition, coverage, and my-secrets endpoints. Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
2f8bab01bc |
Implement user-secret runtime responsibility gates
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
Dotta
|
4e8cbf13e3 | Implement user-specific secret service routes | ||
|
DottaandPaperclip
|
9346994b27 |
Add user-specific secret contracts
Co-Authored-By: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
ac9a883f8b |
Expire ask-user questions superseded by comments (#8799)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work
> - Issue-thread interactions are how agents ask board users for typed
decisions and structured answers inside an issue thread
> - Confirmation interactions already become stale when a later
board/user comment supersedes the pending decision
> - Question interactions had the same workflow risk, because a
board/user could answer in a comment while the old question card stayed
pending
> - This pull request extends the supersede-by-comment lifecycle to
ask-user-question interactions and makes that status visible in the UI
> - The benefit is agents get a clear continuation signal and users do
not see stale question forms after the discussion has moved on

## Linked Issues or Issue Description

No exact public GitHub issue was found.

Bug report:

**Pre-submission checklist**

- [x] I have searched existing open and closed issues and this is not a
duplicate.
- [x] I am on the latest released version of Paperclip, or can reproduce
on `master`.
- [x] I have confirmed the error originates in Paperclip itself, not in
an agent adapter, API provider, or local configuration.

**What happened?**

Pending `ask_user_questions` interactions could remain open after a
later board/user comment changed or answered the request in-thread. That
left a stale form visible and kept the interaction in a pending state
even though the discussion had moved on.

**Expected behavior**

Question interactions should follow the same default
supersede-on-comment behavior as confirmation interactions, with an
explicit expired result that points to the superseding comment.

**Steps to reproduce**

1. Create an `ask_user_questions` interaction on an issue.
2. Add a board/user comment created at or after that interaction.
3. Observe that before this change, the question interaction stayed
pending instead of expiring as superseded by the comment.

**Paperclip version or commit**

Current `master` before this PR.

**Deployment mode**

Self-hosted server or local dev. The bug is in shared issue-thread
interaction lifecycle handling.

**Installation method**

Built from source.

**Agent adapter(s) involved**

Not adapter-specific. This is a core issue-thread interaction bug.

**Database mode**

Applies to the normal Paperclip database-backed interaction lifecycle.

**Access context**

Board user comments supersede agent-created questions.

**Relevant logs or output**

No crash output. The stale pending interaction was visible in the issue
thread state.

**Relevant config (if applicable)**

None.

**Additional context**

Confirmation-style interactions already supported this stale-by-comment
behavior. This PR brings question interactions into the same lifecycle
model.

**Privacy checklist**

- [x] I have reviewed all pasted output for PII and included no private
instance links, local ticket ids, secrets, logs, or screenshots.

## What Changed

- Added `supersedeOnUserComment` support to `ask_user_questions`
payloads, defaulting it to `true` during interaction creation.
- Expire pending question interactions when a later board/user comment
supersedes them, including a result with `expirationReason:
"superseded_by_comment"` and the superseding `commentId`.
- Updated interaction summaries and cards so expired question requests
show a clear amber state with a jump link to the comment and correct
singular/plural copy.
- Updated agent onboarding guidance to describe the new default and how
to opt out.
- Added shared, server, and UI test coverage for the new lifecycle
behavior.

## Verification

- `pnpm exec vitest run
packages/shared/src/issue-thread-interactions.test.ts
server/src/__tests__/issue-thread-interaction-routes.test.ts
server/src/__tests__/issue-thread-interactions-service.test.ts
ui/src/components/IssueThreadInteractionCard.test.tsx
ui/src/lib/issue-thread-interactions.test.ts --reporter=dot` passed: 5
files, 73 tests.
- `pnpm --filter @paperclipai/shared typecheck && pnpm --filter
@paperclipai/server typecheck && pnpm --filter @paperclipai/ui
typecheck` passed.
- `pnpm exec vitest run
server/src/__tests__/issue-thread-interactions-service.test.ts
--reporter=dot && pnpm --filter @paperclipai/server typecheck` passed
after the final type-safety cleanup.
- Confirmed the branch is rebased on current `origin/master`.
- Confirmed the diff does not touch `pnpm-lock.yaml`,
`.github/workflows`, or database migrations.

## Risks

- Low-to-medium risk: `ask_user_questions` now defaults to expiring
after later board/user comments. Existing callers that need questions to
stay open through discussion can set `supersedeOnUserComment: false`.
- Expired question interactions store an empty `answers` array, so
downstream consumers should treat the explicit `expirationReason` as the
meaningful outcome.

> For core feature work, check [`ROADMAP.md`](ROADMAP.md) first and
discuss it in `#dev` before opening the PR. Feature PRs that overlap
with planned core work may need to be redirected — check the roadmap
first. See `CONTRIBUTING.md`.

## Model Used

OpenAI Codex, GPT-5-based coding agent in Paperclip CodexCoder runtime,
with terminal and repository tool use. Exact context window is not
exposed in this runtime.

## Checklist

- [x] I have included a thinking path that traces from project context
to this change
- [x] I have specified the model used (with version and capability
details)
- [x] I have checked ROADMAP.md and confirmed this PR does not duplicate
planned core work
- [x] I have searched GitHub for duplicate or related PRs and linked
them above
- [x] I have either (a) linked existing issues with `Fixes: #` / `Closes
#` / `Refs #` OR (b) described the issue in-PR following the relevant
issue template
- [x] I have not referenced internal/instance-local Paperclip issues or
links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip`
URLs)
- [x] My branch name describes the change (e.g. `docs/...`, `fix/...`)
and contains no internal Paperclip ticket id or instance-derived details
- [x] I have run tests locally and they pass
- [x] I have added or updated tests where applicable
- [x] I have updated relevant documentation to reflect my changes
- [x] I have considered and documented any risks above
- [x] All Paperclip CI gates are green
- [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups
- [x] I will address all Greptile and reviewer comments before
requesting merge

---------

Co-authored-by: Paperclip <noreply@paperclip.ing>
canary/v2026.701.0-canary.0 |
||
|
|
a8f0ebaa80 |
Refresh run config before reusing workspaces (#8797)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work.
> - Agent runs are assembled by the heartbeat service from agent config,
project workspaces, environment config, secret bindings, skills, and
runtime session state.
> - The heartbeat service intentionally reuses adapter sessions,
execution workspaces, and sandbox leases when that preserves useful
state.
> - Reuse becomes incorrect when the effective next-run config changes
after a saved session, workspace, or lease was created.
> - Stale reuse can make a later run appear pinned to old agent,
environment, secret, instruction, or workspace settings.
> - This pull request records non-sensitive fingerprints for the
effective session, workspace, and lease config at run boundaries.
> - When those fingerprints drift, Paperclip refreshes persisted runtime
config or starts fresh execution instead of reusing stale state.
> - The benefit is predictable next-run config freshness without storing
raw secret values, full env maps, provider credentials, or private path
details.

## Linked Issues or Issue Description

- Refs #8058
- Related PRs checked during dedup search: #4968, #4155, #84, #8480.
These cover nearby workspace/session routing or model-config freshness
areas, but do not duplicate this effective run config fingerprinting
path.

## What Changed

- Added effective run config fingerprinting for session, workspace, and
lease reuse decisions, with canonicalization that ignores generated
runtime noise and redacts sensitive values.
- Updated heartbeat reuse logic to compare stored and next-run
fingerprints, reset stale saved sessions, refresh persisted workspace
config snapshots, replace stale reused workspaces when required, and
avoid stale sandbox lease reuse.
- Included plain environment value drift via value hashes, without
storing the raw env values.
- Root-bound instruction content hashing so legacy direct absolute
instruction paths are represented but not read for config fingerprints.
- Batched secret/version metadata lookups for environment lease
fingerprinting.
- Added workspace operation/run result freshness metadata so operators
can inspect non-sensitive decision categories.
- Surfaced config freshness labels and next-run copy in the UI and docs.
- Added focused coverage for fingerprint redaction, session reset
decisions, workspace refresh/replace behavior, environment lease drift,
and persisted workspace restoration.

## Verification

- `git diff --check`
- Sensitive-data scan before push:
- `git diff --unified=0 origin/master...HEAD | rg -n --pcre2
"(AWS_ACCESS_KEY_ID|AWS_SECRET_ACCESS_KEY|ghp_[A-Za-z0-9_]{20,}|github_pat_[A-Za-z0-9_]{20,}|sk-[A-Za-z0-9]{20,}|-----BEGIN
(RSA |OPENSSH |EC |DSA )?PRIVATE KEY-----|AKIA[0-9A-Z]{16})"`
- `git diff --unified=0 origin/master...HEAD | rg -n --pcre2
"[A-Za-z0-9._%+-]+@[A-Za-z0-9.-]+\\.[A-Za-z]{2,}"`
- `pnpm exec vitest run
server/src/__tests__/effective-run-config-fingerprints.test.ts
server/src/__tests__/heartbeat-workspace-session.test.ts
server/src/__tests__/environment-runtime.test.ts`
- `pnpm --filter @paperclipai/server typecheck`
- `pnpm -r typecheck`
- `pnpm --filter @paperclipai/db clean`
- `pnpm test:run`
- `pnpm build`
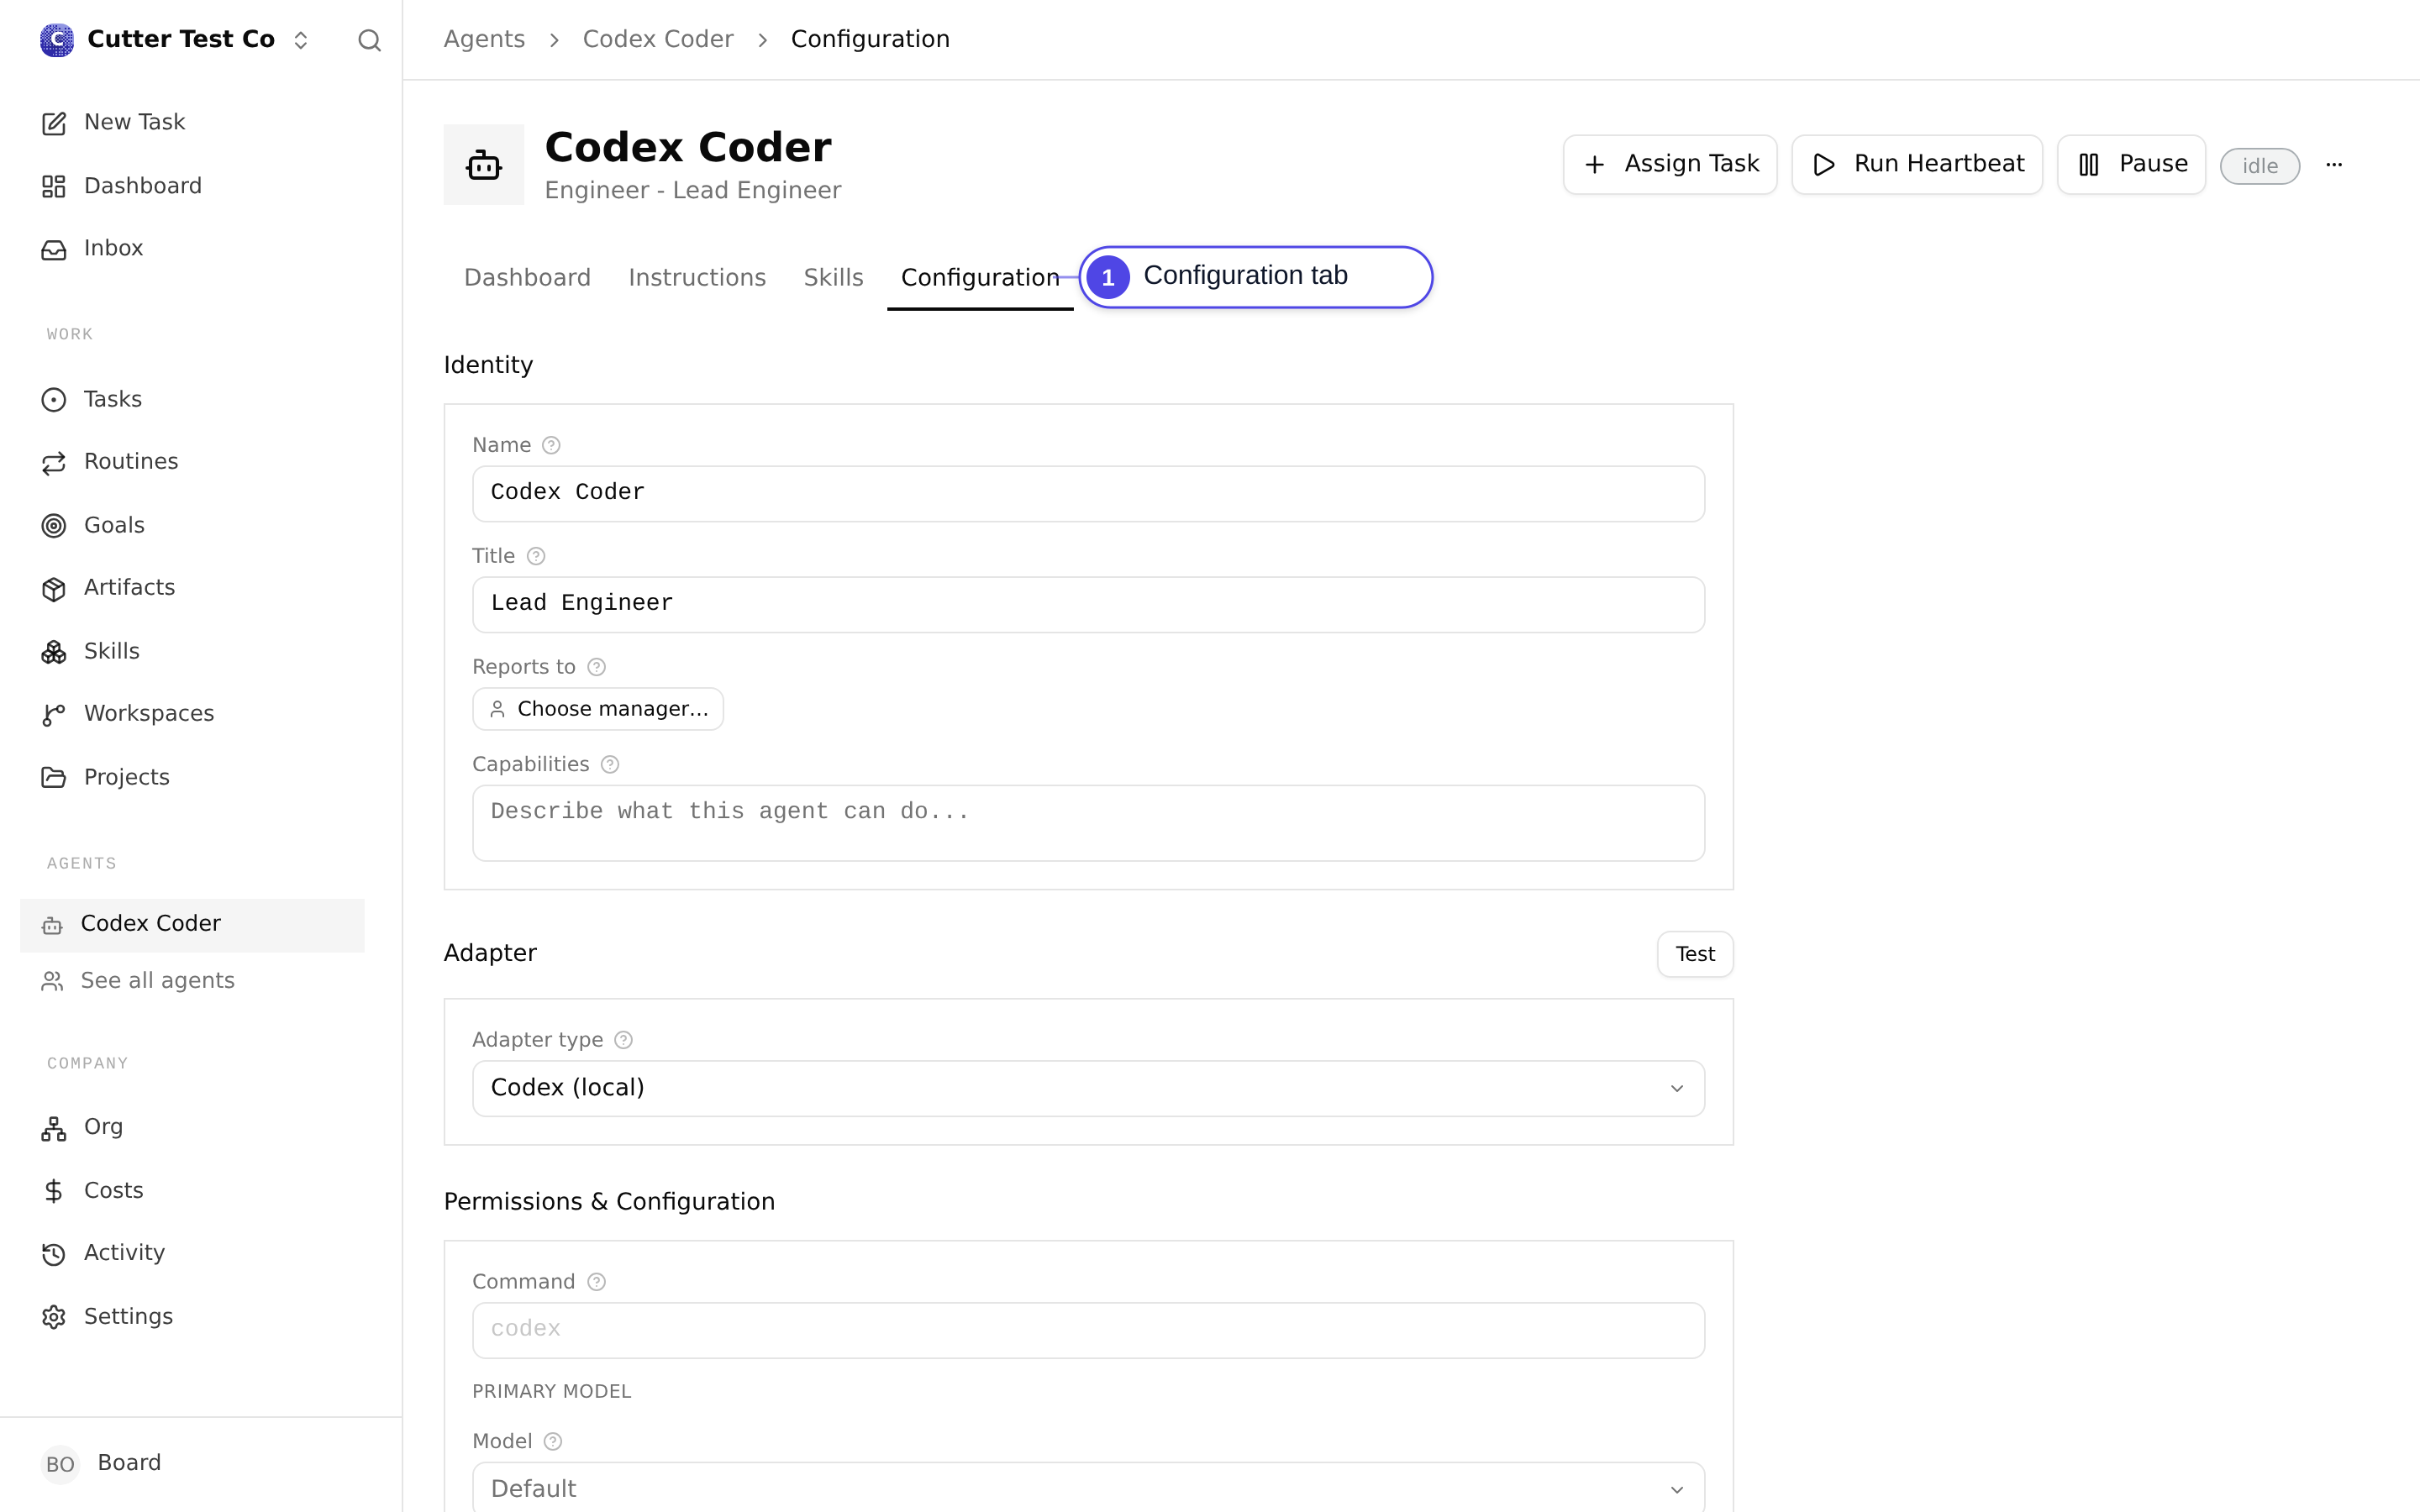
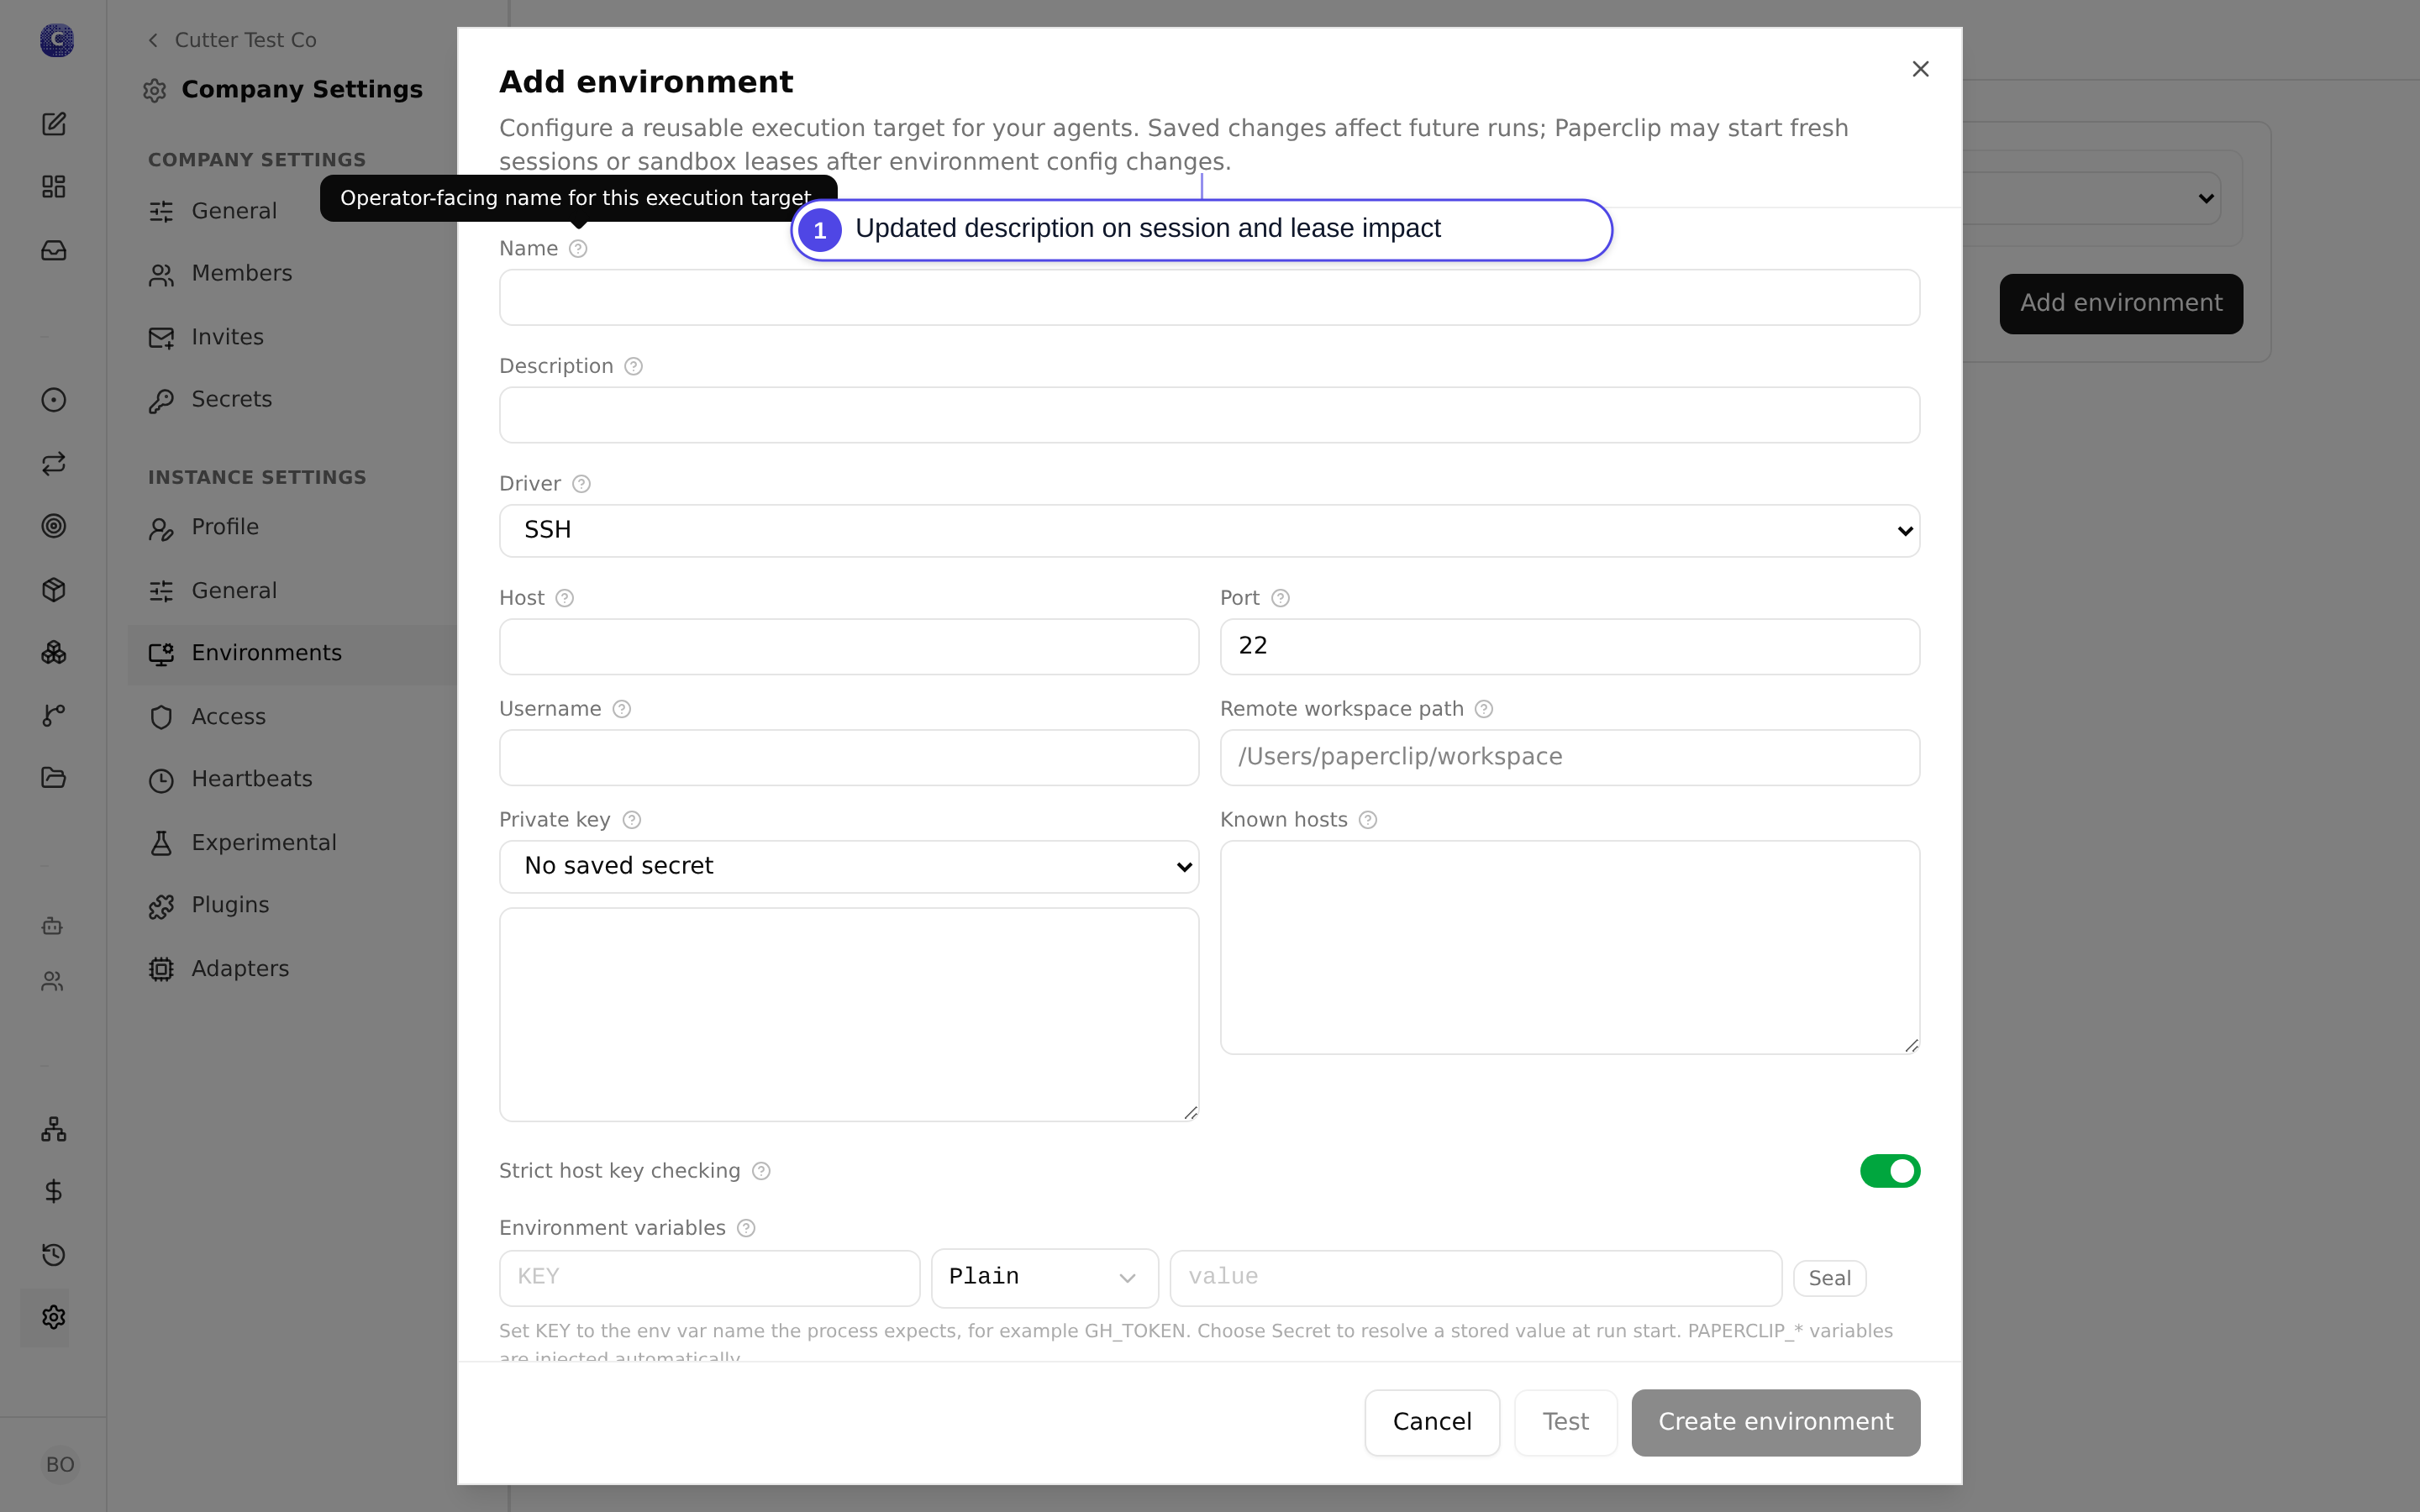
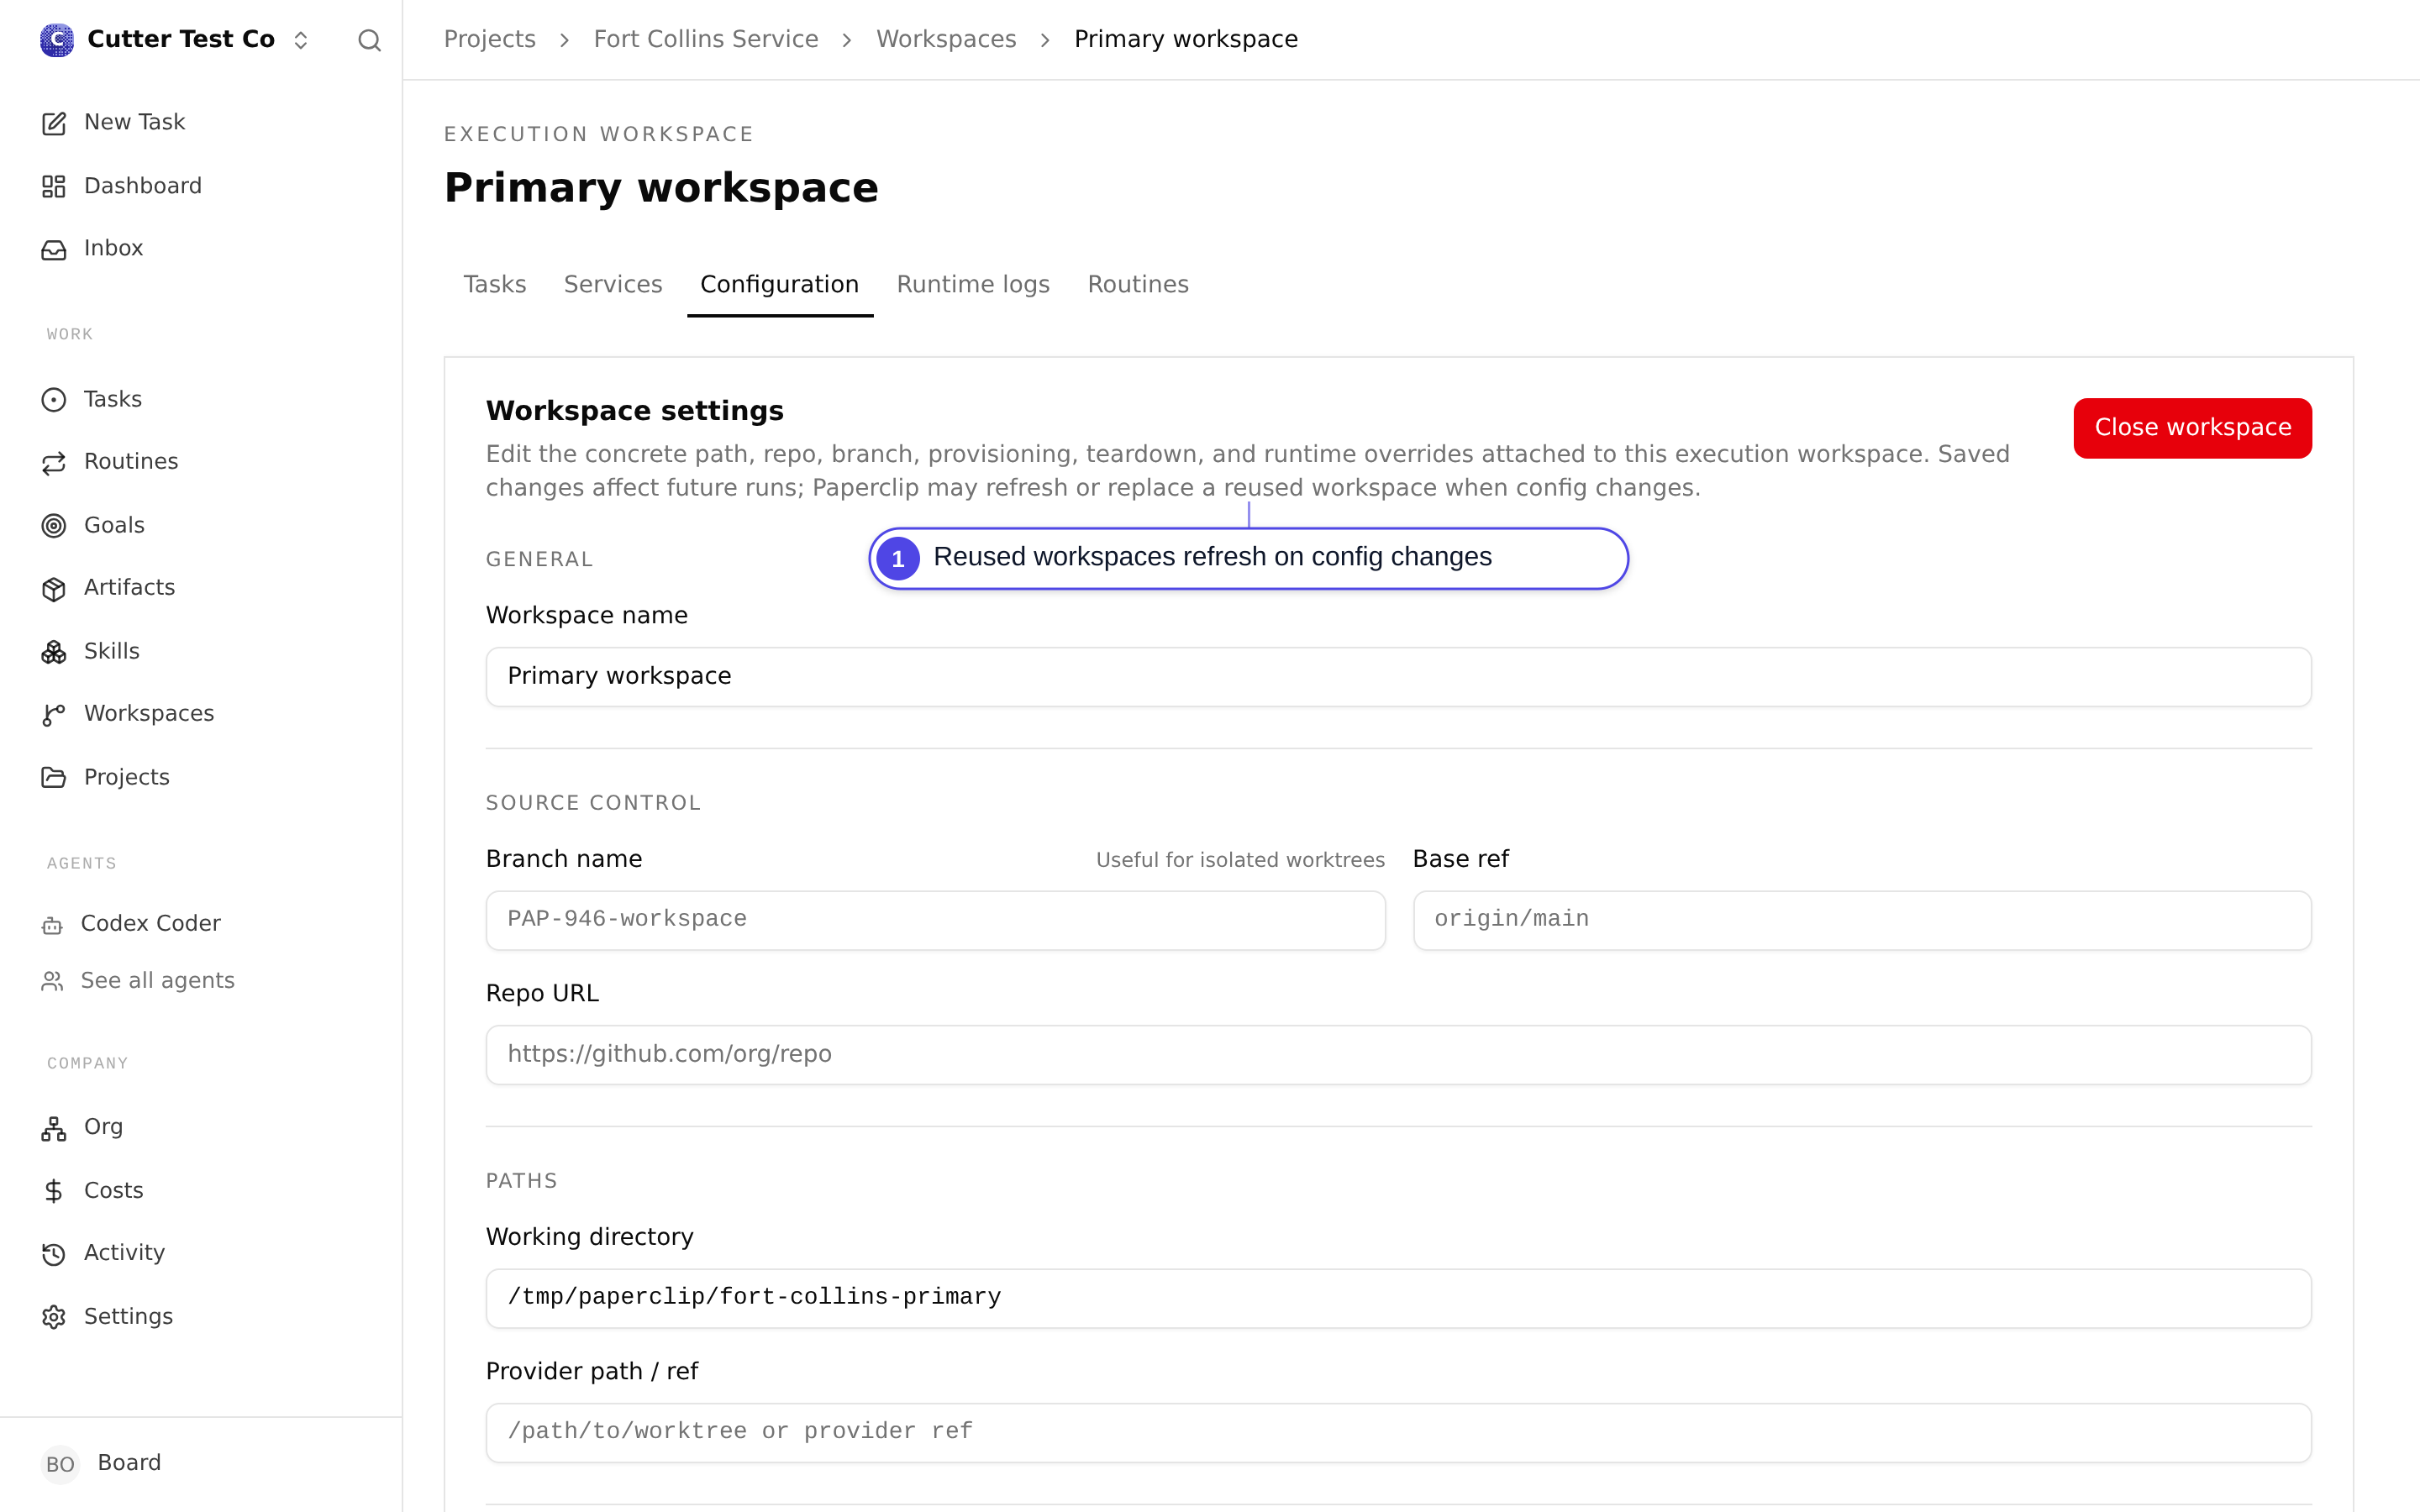
- UI screenshots from Cutter:
-
https://artifacts.cutter.sh/8797/run-2f4827c-2026-06-30T18-57-25/preview/change-01.png
-
https://artifacts.cutter.sh/8797/run-2f4827c-2026-06-30T18-57-25/preview/change-02.png
-
https://artifacts.cutter.sh/8797/run-2f4827c-2026-06-30T18-57-25/preview/change-03.png

## Risks

- Medium: overly broad fingerprints could start fresh sessions,
workspaces, or sandbox leases more often than necessary.
- Medium: missing a config category would allow stale reuse to persist
for that category.
- Medium: legacy direct absolute instruction paths are no longer
content-hashed unless they are paired with an absolute managed
instructions root.
- Low data risk: fingerprint metadata stores hashes and category names,
not raw secrets, raw env values, provider credentials, or private path
details.

> For core feature work, check [`ROADMAP.md`](ROADMAP.md) first and
discuss it in `#dev` before opening the PR. Feature PRs that overlap
with planned core work may need to be redirected — check the roadmap
first. See `CONTRIBUTING.md`.

## Model Used

OpenAI GPT-5 via Codex CLI / Codex coding agent, tool-enabled with
shell, Git, GitHub CLI, local test execution, and code editing. The
exact deployed model variant and context window are not exposed by this
environment.

## Checklist

- [x] I have included a thinking path that traces from project context
to this change
- [x] I have specified the model used (with version and capability
details)
- [x] I have checked ROADMAP.md and confirmed this PR does not duplicate
planned core work
- [x] I have searched GitHub for duplicate or related PRs and linked
them above
- [x] I have either (a) linked existing issues with `Fixes: #` / `Closes
#` / `Refs #` OR (b) described the issue in-PR following the relevant
issue template
- [x] I have not referenced internal/instance-local Paperclip issues or
links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip`
URLs)
- [x] My branch name describes the change (e.g. `docs/...`, `fix/...`)
and contains no internal Paperclip ticket id or instance-derived details
- [x] I have run tests locally and they pass
- [x] I have added or updated tests where applicable
- [x] I have updated relevant documentation to reflect my changes
- [x] I have considered and documented any risks above
- [x] All Paperclip CI gates are green
- [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups
- [x] I will address all Greptile and reviewer comments before
requesting merge

---------

Co-authored-by: Paperclip <noreply@paperclip.ing>
Co-authored-by: Cody <cody@paperclip.ing>
canary/v2026.630.0-canary.7 |
||
|
dependabot[bot]
|
5bd6c6ec3c |
build(deps): bump acpx from 0.6.1 to 0.11.2 (#8741)
Bumps [acpx](https://github.com/openclaw/acpx) from 0.6.1 to 0.11.2. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/openclaw/acpx/releases">acpx's releases</a>.</em></p> <blockquote> <h2>acpx 0.11.0</h2> <h2>v0.11.0</h2> <h3>Changes</h3> <ul> <li>Agents/built-ins: bump the default Claude ACP adapter range to <code>@agentclientprotocol/claude-agent-acp@^0.37.0</code>. Thanks <a href="https://github.com/trumpyla"><code>@trumpyla</code></a>.</li> <li>Runtime/embedding: surface cost, token usage breakdowns, and advertised command metadata on runtime status/events. Thanks <a href="https://github.com/DaniAkash"><code>@DaniAkash</code></a>.</li> <li>Agents/built-ins: add <code>fast-agent</code> as a built-in fast-agent ACP adapter via <code>uvx fast-agent-mcp acp</code>.</li> <li>Agents/built-ins: add <code>mux</code> as a built-in coder/mux ACP adapter via <code>npx -y mux@^0.27.0 acp</code>. Thanks <a href="https://github.com/ThomasK33"><code>@ThomasK33</code></a>.</li> <li>CLI: add <code>acpx compare</code> to run one prompt across multiple agents and summarize timing, token usage, stop reason, permissions, and final output side by side. Thanks <a href="https://github.com/mvanhorn"><code>@mvanhorn</code></a>.</li> </ul> <h3>Fixes</h3> <ul> <li>CLI/Claude: isolate built-in Claude ACP sessions from user settings by default so globally enabled channel and daemon plugins cannot interfere with a spawned session. Set <code>ACPX_CLAUDE_INCLUDE_USER_SETTINGS=1</code> to restore user settings deliberately. Fixes <a href="https://redirect.github.com/openclaw/acpx/issues/361">#361</a>.</li> <li>ACP/models: support SDK 0.25 model config options while preserving <code>session/set_model</code> compatibility for adapters that explicitly advertise legacy model metadata.</li> <li>CLI/Claude: let Claude Code adjudicate model selectors missing from a stale advertised model list on later persistent turns, and preserve the adapter-reported current model after model switches. Thanks <a href="https://github.com/oakif"><code>@oakif</code></a>.</li> <li>Client/ACP: advertise scoped Devin/Windsurf-compatible client metadata and handle Devin extension requests/notifications without noisy method-not-found logs. Thanks <a href="https://github.com/LivioGama"><code>@LivioGama</code></a>.</li> <li>Runtime/sessions: treat corrupt public file-session records as missing while preserving genuine filesystem errors. Thanks <a href="https://github.com/KrasimirKralev"><code>@KrasimirKralev</code></a>.</li> </ul> <h3>Verification</h3> <ul> <li>npm: <a href="https://www.npmjs.com/package/acpx/v/0.11.0">https://www.npmjs.com/package/acpx/v/0.11.0</a></li> <li>Registry tarball: <a href="https://registry.npmjs.org/acpx/-/acpx-0.11.0.tgz">https://registry.npmjs.org/acpx/-/acpx-0.11.0.tgz</a></li> <li>Integrity: <code>sha512-l42LJFmd6kvbr1UytvwWmr5Mdy/v9l3FM6Necs01PWbjUIkxjCdxg97duqoRfRqxtDAfnNPb1IlgIf2ZgMZQqA==</code></li> <li>Candidate CI: <a href="https://github.com/openclaw/acpx/actions/runs/27676359224">https://github.com/openclaw/acpx/actions/runs/27676359224</a></li> <li>Trusted publish: <a href="https://github.com/openclaw/acpx/actions/runs/27676823793">https://github.com/openclaw/acpx/actions/runs/27676823793</a></li> <li>Packed CLI and real Codex ACP adapter E2E passed before tagging.</li> </ul> <h2>2026.5.23 (v0.10.0)</h2> <h3>Changes</h3> <ul> <li>CLI/sessions: add <code>sessions export</code> and <code>sessions import</code> for moving portable session archives between machines. Thanks <a href="https://github.com/mvanhorn"><code>@mvanhorn</code></a>.</li> </ul> <h3>Release Proof</h3> <ul> <li>npm: <a href="https://www.npmjs.com/package/acpx/v/0.10.0">https://www.npmjs.com/package/acpx/v/0.10.0</a></li> <li>registry tarball: <a href="https://registry.npmjs.org/acpx/-/acpx-0.10.0.tgz">https://registry.npmjs.org/acpx/-/acpx-0.10.0.tgz</a></li> <li>integrity: <code>sha512-hd48XV03gG3sd409T1lDrOKJTTz1ap4g0wrndXjxQ590tN85pBYlvfNLyerybvGRrtUGsZjNdt99r1jpIt6ukA==</code></li> <li>release workflow: <a href="https://github.com/openclaw/acpx/actions/runs/26323055145">https://github.com/openclaw/acpx/actions/runs/26323055145</a></li> <li>CI: <a href="https://github.com/openclaw/acpx/actions/runs/26323053524">https://github.com/openclaw/acpx/actions/runs/26323053524</a></li> </ul> <h2>2026.5.22 (v0.9.0)</h2> <h3>Changes</h3> <ul> <li>Tooling: add Slophammer TypeScript quality gates for coverage, complexity, unsafe types, mutation testing, DRY checks, and dependency boundaries.</li> <li>Agents/built-ins: switch the default Codex adapter to <code>@agentclientprotocol/codex-acp</code>, with Codex model selection handled through advertised ACP model ids, and bump the default Claude ACP adapter range.</li> <li>Tooling: add a repo-local autoreview skill and helper for Codex-first</li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/openclaw/acpx/blob/main/CHANGELOG.md">acpx's changelog</a>.</em></p> <blockquote> <h2>2026.6.23 (v0.11.2)</h2> <h3>Changes</h3> <h3>Breaking</h3> <h3>Fixes</h3> <ul> <li>Runtime/status: persist token usage reported on successful prompt responses, including adapters that only provide a sparse <code>usage_update</code>.</li> </ul> <h2>Unreleased</h2> <h3>Changes</h3> <h3>Breaking</h3> <h3>Fixes</h3> <h2>2026.6.23 (v0.11.1)</h2> <h3>Changes</h3> <ul> <li>Runtime/embedding: preserve per-agent environment variables across ACP session creation, queue handoff, persistence, and reconnects. Thanks <a href="https://github.com/zhangguiping-xydt"><code>@zhangguiping-xydt</code></a>.</li> </ul> <h3>Breaking</h3> <h3>Fixes</h3> <ul> <li>CLI/queue: harden command parsing, queue-owner startup, stale process cleanup, and release/CI checks found by <code>clawpatch</code>.</li> <li>Windows/Claude: only export a native <code>.exe</code> as <code>CLAUDE_CODE_EXECUTABLE</code>; unresolved <code>.cmd</code>, <code>.bat</code>, and <code>.ps1</code> shims now fall back to the Claude ACP adapter's bundled native binary. Fixes <a href="https://redirect.github.com/openclaw/openclaw/issues/93465">openclaw/openclaw#93465</a>.</li> <li>Client/ACP: ignore non-object JSON lines from adapter stdout before ACP dispatch, preventing primitive frames from crashing the SDK message path.</li> <li>ACP/models: call the current SDK <code>session/set_model</code> method for legacy model metadata instead of the generic extension fallback.</li> <li>CLI/config: add <code>--mcp-config</code> for session-scoped MCP servers without writing a project config file. Live persistent sessions reject MCP config changes until closed. Fixes <a href="https://redirect.github.com/openclaw/acpx/issues/387">#387</a>.</li> </ul> <h2>2026.6.17 (v0.11.0)</h2> <h3>Changes</h3> <ul> <li>Agents/built-ins: bump the default Claude ACP adapter range to <code>@agentclientprotocol/claude-agent-acp@^0.37.0</code>. Thanks <a href="https://github.com/trumpyla"><code>@trumpyla</code></a>.</li> <li>Runtime/embedding: surface cost, token usage breakdowns, and advertised command metadata on runtime status/events. Thanks <a href="https://github.com/DaniAkash"><code>@DaniAkash</code></a>.</li> <li>Agents/built-ins: add <code>fast-agent</code> as a built-in fast-agent ACP adapter via <code>uvx fast-agent-mcp acp</code>.</li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/openclaw/acpx/commits/v0.11.2">compare view</a></li> </ul> </details> <br /> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>canary/v2026.630.0-canary.6 |
||
|
dependabot[bot]
|
c06e2be21a |
build(deps): bump @tailwindcss/typography from 0.5.19 to 0.5.20 (#8738)
Bumps [@tailwindcss/typography](https://github.com/tailwindlabs/tailwindcss-typography) from 0.5.19 to 0.5.20. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/tailwindlabs/tailwindcss-typography/releases">@tailwindcss/typography's releases</a>.</em></p> <blockquote> <h2>v0.5.20</h2> <h3>Fixed</h3> <ul> <li>Support installing with stable versions of Tailwind CSS v4 (<a href="https://redirect.github.com/tailwindlabs/tailwindcss-typography/pull/424">#424</a>)</li> </ul> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/tailwindlabs/tailwindcss-typography/blob/main/CHANGELOG.md">@tailwindcss/typography's changelog</a>.</em></p> <blockquote> <h2>[0.5.20] - 2026-06-08</h2> <h3>Fixed</h3> <ul> <li>Support installing with stable versions of Tailwind CSS v4 (<a href="https://redirect.github.com/tailwindlabs/tailwindcss-typography/pull/424">#424</a>)</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/tailwindlabs/tailwindcss-typography/commit/e3714a3fe55551ce9d51eec4721183ed6b1d5cd1"><code>e3714a3</code></a> 0.5.20</li> <li><a href="https://github.com/tailwindlabs/tailwindcss-typography/commit/f34283d2961e18dd0dc2a849702e0dfd45fc80cb"><code>f34283d</code></a> Update tailwindcss peer dependency version (<a href="https://redirect.github.com/tailwindlabs/tailwindcss-typography/issues/424">#424</a>)</li> <li><a href="https://github.com/tailwindlabs/tailwindcss-typography/commit/543de4274390e90c4aab5d216729b46a3ba5541b"><code>543de42</code></a> bump Node.js</li> <li><a href="https://github.com/tailwindlabs/tailwindcss-typography/commit/881b0488df9fd05e5361276b66a9ee8e7f39a3a7"><code>881b048</code></a> Setup OIDC (<a href="https://redirect.github.com/tailwindlabs/tailwindcss-typography/issues/423">#423</a>)</li> <li><a href="https://github.com/tailwindlabs/tailwindcss-typography/commit/74a3da779bb43e4e68f446395224c768704c1fb6"><code>74a3da7</code></a> Fix typo in README.md (<a href="https://redirect.github.com/tailwindlabs/tailwindcss-typography/issues/413">#413</a>)</li> <li><a href="https://github.com/tailwindlabs/tailwindcss-typography/commit/3963dfede4845f46451db1863fd5321f4cdea03b"><code>3963dfe</code></a> Bump js-yaml from 3.14.1 to 3.14.2 (<a href="https://redirect.github.com/tailwindlabs/tailwindcss-typography/issues/410">#410</a>)</li> <li><a href="https://github.com/tailwindlabs/tailwindcss-typography/commit/abf85cc6e1b4f9b914b0f66453e5a97a9899a15c"><code>abf85cc</code></a> className instead of classname (<a href="https://redirect.github.com/tailwindlabs/tailwindcss-typography/issues/406">#406</a>)</li> <li>See full diff in <a href="https://github.com/tailwindlabs/tailwindcss-typography/compare/v0.5.19...v0.5.20">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~GitHub%20Actions">GitHub Actions</a>, a new releaser for <code>@tailwindcss/typography</code> since your current version.</p> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
8f3fa07d59 |
build(deps): bump @pierre/diffs from 1.1.22 to 1.2.11 (#8744)
Bumps @pierre/diffs from 1.1.22 to 1.2.11. [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
b755ab55fd |
build(deps): bump multer from 2.1.1 to 2.2.0 (#8743)
Bumps [multer](https://github.com/expressjs/multer) from 2.1.1 to 2.2.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/expressjs/multer/releases">multer's releases</a>.</em></p> <blockquote> <h2>v2.2.0</h2> <h2>Important</h2> <ul> <li>Fix <a href="https://www.cve.org/CVERecord?id=CVE-2026-5038">CVE-2026-5038</a> (<a href="https://github.com/expressjs/multer/security/advisories/GHSA-3p4h-7m6x-2hcm">GHSA-3p4h-7m6x-2hcm</a>)</li> <li>Fix <a href="https://www.cve.org/CVERecord?id=CVE-2026-5079">CVE-2026-5079</a> (<a href="https://github.com/expressjs/multer/security/advisories/GHSA-72gw-mp4g-v24j">GHSA-72gw-mp4g-v24j</a>)</li> </ul> <h2>What's Changed</h2> <ul> <li>chore(deps): bump actions/upload-artifact from 7.0.0 to 7.0.1 by <a href="https://github.com/dependabot"><code>@dependabot</code></a>[bot] in <a href="https://redirect.github.com/expressjs/multer/pull/1397">expressjs/multer#1397</a></li> <li>chore(deps): bump github/codeql-action from 4.32.4 to 4.36.1 by <a href="https://github.com/dependabot"><code>@dependabot</code></a>[bot] in <a href="https://redirect.github.com/expressjs/multer/pull/1409">expressjs/multer#1409</a></li> <li>chore(deps): bump actions/checkout from 6.0.2 to 6.0.3 by <a href="https://github.com/dependabot"><code>@dependabot</code></a>[bot] in <a href="https://redirect.github.com/expressjs/multer/pull/1410">expressjs/multer#1410</a></li> <li>ci: add Node 26 to test matrix by <a href="https://github.com/gameroman"><code>@gameroman</code></a> in <a href="https://redirect.github.com/expressjs/multer/pull/1404">expressjs/multer#1404</a></li> <li>Release: 2.2.0 by <a href="https://github.com/UlisesGascon"><code>@UlisesGascon</code></a> in <a href="https://redirect.github.com/expressjs/multer/pull/1412">expressjs/multer#1412</a></li> </ul> <h2>New Contributors</h2> <ul> <li><a href="https://github.com/gameroman"><code>@gameroman</code></a> made their first contribution in <a href="https://redirect.github.com/expressjs/multer/pull/1404">expressjs/multer#1404</a></li> </ul> <p><strong>Full Changelog</strong>: <a href="https://github.com/expressjs/multer/compare/v2.1.1...v2.2.0">https://github.com/expressjs/multer/compare/v2.1.1...v2.2.0</a></p> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/expressjs/multer/blob/main/CHANGELOG.md">multer's changelog</a>.</em></p> <blockquote> <h2>2.2.0</h2> <ul> <li>Fix <a href="https://www.cve.org/CVERecord?id=CVE-2026-5038">CVE-2026-5038</a> (<a href="https://github.com/expressjs/multer/security/advisories/GHSA-3p4h-7m6x-2hcm">GHSA-3p4h-7m6x-2hcm</a>)</li> <li>Fix <a href="https://www.cve.org/CVERecord?id=CVE-2026-5079">CVE-2026-5079</a> (<a href="https://github.com/expressjs/multer/security/advisories/GHSA-72gw-mp4g-v24j">GHSA-72gw-mp4g-v24j</a>)</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/expressjs/multer/commit/2e2af08157c66cbbc76539ccbd8869097a0c8feb"><code>2e2af08</code></a> 2.2.0 (<a href="https://redirect.github.com/expressjs/multer/issues/1412">#1412</a>)</li> <li><a href="https://github.com/expressjs/multer/commit/a192b5278f240967f5eb13dd1e9a413b4e1b6533"><code>a192b52</code></a> feat: add fieldNestingDepth limit option</li> <li><a href="https://github.com/expressjs/multer/commit/9c801c7136fdaa8437b84c6455cd46a3467a8058"><code>9c801c7</code></a> fix: clean up in-progress disk writes on abort</li> <li><a href="https://github.com/expressjs/multer/commit/0adb21d0294fe7315344feb6ddee00b0666d9e8a"><code>0adb21d</code></a> ci: add Node 26 to test matrix (<a href="https://redirect.github.com/expressjs/multer/issues/1404">#1404</a>)</li> <li><a href="https://github.com/expressjs/multer/commit/f5e17c39c818edade71b4deec7d114fdaafd54af"><code>f5e17c3</code></a> chore(deps): bump actions/checkout from 6.0.2 to 6.0.3 (<a href="https://redirect.github.com/expressjs/multer/issues/1410">#1410</a>)</li> <li><a href="https://github.com/expressjs/multer/commit/de1fefd9d201f0ae48f1de056f00a349dd12f9bc"><code>de1fefd</code></a> chore(deps): bump github/codeql-action from 4.32.4 to 4.36.1 (<a href="https://redirect.github.com/expressjs/multer/issues/1409">#1409</a>)</li> <li><a href="https://github.com/expressjs/multer/commit/67abfc89f4caa5f842eb75083ddb3854db4cc38a"><code>67abfc8</code></a> chore(deps): bump actions/upload-artifact from 7.0.0 to 7.0.1 (<a href="https://redirect.github.com/expressjs/multer/issues/1397">#1397</a>)</li> <li>See full diff in <a href="https://github.com/expressjs/multer/compare/v2.1.1...v2.2.0">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
c5a47c1fd9 |
build(deps): bump mermaid from 11.12.3 to 11.16.0 (#8740)
Bumps [mermaid](https://github.com/mermaid-js/mermaid) from 11.12.3 to 11.16.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/mermaid-js/mermaid/releases">mermaid's releases</a>.</em></p> <blockquote> <h2>mermaid@11.16.0</h2> <h3>Minor Changes</h3> <ul> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7535">#7535</a> <a href="https://github.com/mermaid-js/mermaid/commit/ea1c48f53fce5d025388d386c90da8743ee25b13"><code>ea1c48f</code></a> Thanks <a href="https://github.com/ragelink"><code>@ragelink</code></a>! - feat(cynefin): Adds the Cynefin framework as a new diagram type (beta) to Mermaid (available as <code>cynefin-beta</code>). The Cynefin framework, created by Dave Snowden, is a decision-making framework that categorizes problems into five complexity domains, widely used in agile, incident management, strategy, and organizational design.</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7721">#7721</a> <a href="https://github.com/mermaid-js/mermaid/commit/f45cc2cc5683b90990e374a463b7bcad0fd68a38"><code>f45cc2c</code></a> Thanks <a href="https://github.com/notionparallax"><code>@notionparallax</code></a>! - feat(treeView): add box-drawing character input support for treeView diagrams</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7550">#7550</a> <a href="https://github.com/mermaid-js/mermaid/commit/f1f4d45ee0513b64a2bd280087d31656f9d2c786"><code>f1f4d45</code></a> Thanks <a href="https://github.com/DominicBurkart"><code>@DominicBurkart</code></a>! - feat(xychart): add per-point text labels for xychart line plots</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7527">#7527</a> <a href="https://github.com/mermaid-js/mermaid/commit/b4d0442dd1628acb3f71681519e7f47fc8bacf55"><code>b4d0442</code></a> Thanks <a href="https://github.com/notionparallax"><code>@notionparallax</code></a>! - feat(treeView): Extends the existing treeView-beta diagram with features useful for representing file/directory structures.</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7793">#7793</a> <a href="https://github.com/mermaid-js/mermaid/commit/a6f097d580d459dfc3ade3e21030037341f79940"><code>a6f097d</code></a> Thanks <a href="https://github.com/SSDWGG"><code>@SSDWGG</code></a>! - feat(er): support optional ER attribute types with a <code>?</code> suffix</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7772">#7772</a> <a href="https://github.com/mermaid-js/mermaid/commit/37f2e36fa017698b66093ac5518396523a7a3241"><code>37f2e36</code></a> Thanks <a href="https://github.com/devareddy05"><code>@devareddy05</code></a>! - feat(gantt): support multiple <code>excludes</code> / <code>includes</code> lines so long exclusion lists can be split into commented groups (<a href="https://redirect.github.com/mermaid-js/mermaid/issues/6270">#6270</a>)</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7708">#7708</a> <a href="https://github.com/mermaid-js/mermaid/commit/4e63e9d338b6476df283afd4a002072945bc4563"><code>4e63e9d</code></a> Thanks <a href="https://github.com/txmxthy"><code>@txmxthy</code></a>! - feat(architecture): add <code>align row|column {ids…}</code> directive to architecture-beta diagrams so authors can declare horizontal or vertical alignment of services explicitly.</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7760">#7760</a> <a href="https://github.com/mermaid-js/mermaid/commit/05223bee47a424be3ba7805e753b96861d342765"><code>05223be</code></a> Thanks <a href="https://github.com/ngdaniels"><code>@ngdaniels</code></a>! - feat(pie): Enhance Pie Chart - Enable donut chart, Set legend position, and highlight slice</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7251">#7251</a> <a href="https://github.com/mermaid-js/mermaid/commit/216e4e9a61afceae885b00854f79e17373ccad31"><code>216e4e9</code></a> Thanks <a href="https://github.com/ydah"><code>@ydah</code></a>! - feat(railroad): Add support for Railroad Diagrams (Syntax Diagrams) with four input syntaxes: IR (railroad-beta), EBNF (railroad-ebnf-beta), ABNF (railroad-abnf-beta), and PEG (railroad-peg-beta).</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7774">#7774</a> <a href="https://github.com/mermaid-js/mermaid/commit/e5c75e6b797f84f8f652d8771eb1ce6161dd8f89"><code>e5c75e6</code></a> Thanks <a href="https://github.com/ngdaniels"><code>@ngdaniels</code></a>! - feat(xychart): enable rotate label on X-axis</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7791">#7791</a> <a href="https://github.com/mermaid-js/mermaid/commit/974fa7b7e791b442ad5f7862f1cbecd53d982485"><code>974fa7b</code></a> Thanks <a href="https://github.com/knsv-bot"><code>@knsv-bot</code></a>! - feat(swimlane): add swimlane as a standalone diagram type with a dedicated layered orthogonal layout algorithm</p> </li> </ul> <h3>Patch Changes</h3> <ul> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7744">#7744</a> <a href="https://github.com/mermaid-js/mermaid/commit/633c261dadbaa20ee0cf9a0299e2269abe4ca573"><code>633c261</code></a> Thanks <a href="https://github.com/ashishjain0512"><code>@ashishjain0512</code></a>! - fix(architecture): add <code>architecture.seed</code> config option to make architecture diagrams render deterministically. Resolves <a href="https://redirect.github.com/mermaid-js/mermaid/issues/7729">#7729</a>.</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7732">#7732</a> <a href="https://github.com/mermaid-js/mermaid/commit/c8ba156f551e94dd9a5c30b4971fe83ef3538634"><code>c8ba156</code></a> Thanks <a href="https://github.com/rkdfx"><code>@rkdfx</code></a>! - fix: tolerate leading horizontal whitespace before YAML frontmatter delimiters. Closes <a href="https://redirect.github.com/mermaid-js/mermaid/issues/7613">mermaid-js/mermaid#7613</a></p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7314">#7314</a> <a href="https://github.com/mermaid-js/mermaid/commit/4e4e6c4a108d834dd0f643b08deb89159e0eca94"><code>4e4e6c4</code></a> Thanks <a href="https://github.com/darshanr0107"><code>@darshanr0107</code></a>! - fix(flowchart): Prevent crash when flowchart node shape is undefined</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7762">#7762</a> <a href="https://github.com/mermaid-js/mermaid/commit/cfd23916f3c6b3ceafc4c0cfaf4078f6442bbc4f"><code>cfd2391</code></a> Thanks <a href="https://github.com/Dharya-dev"><code>@Dharya-dev</code></a>! - fix(class): support styling and callbacks for generic classes</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7284">#7284</a> <a href="https://github.com/mermaid-js/mermaid/commit/c1f116d36646786326c596a5f25e519bdaac7748"><code>c1f116d</code></a> Thanks <a href="https://github.com/darshanr0107"><code>@darshanr0107</code></a>! - fix(gantt): Render gantt vertical markers without affecting row layout or chart height</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7786">#7786</a> <a href="https://github.com/mermaid-js/mermaid/commit/72fbab1a4d6efbfa219b13c1639dabcadc754ad8"><code>72fbab1</code></a> Thanks <a href="https://github.com/knsv-bot"><code>@knsv-bot</code></a>! - fix(er): allow special characters (e.g. dots) in ER diagram attribute names and types by escaping them with backticks</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7672">#7672</a> <a href="https://github.com/mermaid-js/mermaid/commit/4887e9721c33b5d771306a4e7ab768d78908a157"><code>4887e97</code></a> Thanks <a href="https://github.com/sjackson0109"><code>@sjackson0109</code></a>! - fix(flowchart): respect per-subgraph direction keyword in Dagre layout. Fixes <a href="https://redirect.github.com/mermaid-js/mermaid/issues/4648">#4648</a></p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7734">#7734</a> <a href="https://github.com/mermaid-js/mermaid/commit/a4c1e507a347256f1f3a42be3feb5b6ddc7257f2"><code>a4c1e50</code></a> Thanks <a href="https://github.com/OfirHaf"><code>@OfirHaf</code></a>! - fix(block): read block padding and sanitize config dynamically instead of at module load time</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7674">#7674</a> <a href="https://github.com/mermaid-js/mermaid/commit/cc750896b21a2715256ac0de486bafe0351c40c4"><code>cc75089</code></a> Thanks <a href="https://github.com/cyphercodes"><code>@cyphercodes</code></a>! - fix(block): respect current DOMPurify config when sanitizing labels</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7711">#7711</a> <a href="https://github.com/mermaid-js/mermaid/commit/be2e28201445505ec68b1ebf6e3e6813fb6a6898"><code>be2e282</code></a> Thanks <a href="https://github.com/Jinacker"><code>@Jinacker</code></a>! - fix(flowchart): render flowchart and state self-loop edges as a single SVG path.</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7781">#7781</a> <a href="https://github.com/mermaid-js/mermaid/commit/d945968c13b154dcf2c89ad1e6ed5104458d32fe"><code>d945968</code></a> Thanks <a href="https://github.com/Dharya-dev"><code>@Dharya-dev</code></a>! - fix(radar): align axis labels based on angular position to prevent clipping</p> </li> <li> <p><a href="https://redirect.github.com/mermaid-js/mermaid/pull/7661">#7661</a> <a href="https://github.com/mermaid-js/mermaid/commit/2f5e9e8c9aabb74e61e43428e91217e9585c8d05"><code>2f5e9e8</code></a> Thanks <a href="https://github.com/nabila401"><code>@nabila401</code></a>! - fix(venn): fix 3-circle venn diagram union rendering</p> </li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/mermaid-js/mermaid/commit/7c0cafcf42e76bfaf79d0cbbd12edb986612f014"><code>7c0cafc</code></a> Version Packages: v11.16.0 (<a href="https://redirect.github.com/mermaid-js/mermaid/issues/7916">#7916</a>)</li> <li><a href="https://github.com/mermaid-js/mermaid/commit/26acd1a8c67a5dabc0764ab18d11e3468d1f880f"><code>26acd1a</code></a> Merge pull request <a href="https://redirect.github.com/mermaid-js/mermaid/issues/7915">#7915</a> from mermaid-js/release/11.16.0</li> <li><a href="https://github.com/mermaid-js/mermaid/commit/5a8eae7b0bfd250aa1e48dae26621f452937cd46"><code>5a8eae7</code></a> Merge branch 'master' into release/11.16.0</li> <li><a href="https://github.com/mermaid-js/mermaid/commit/dd5ea777ae6a2b3ddbaac7852f7404f4ca3b3c83"><code>dd5ea77</code></a> Merge pull request <a href="https://redirect.github.com/mermaid-js/mermaid/issues/7913">#7913</a> from mermaid-js/pebr/fix-changesets</li> <li><a href="https://github.com/mermaid-js/mermaid/commit/658ee66388759a8d55038b4f9df3d0aae188f369"><code>658ee66</code></a> docs: fix missing bumps of <code>@mermaid-js/parser</code></li> <li><a href="https://github.com/mermaid-js/mermaid/commit/04259a18ff62f5b793c26236bc753816b7b6dd6a"><code>04259a1</code></a> docs: fix author and commit on examples changeset</li> <li><a href="https://github.com/mermaid-js/mermaid/commit/c9dcfb15e171d0bc526bf6336ac9cce1a726545e"><code>c9dcfb1</code></a> docs: update changeset diagram scopes</li> <li><a href="https://github.com/mermaid-js/mermaid/commit/a34dab9217c5e30b53ef768ed7f19ac439c2f393"><code>a34dab9</code></a> docs: remove swimlane/cynefin bugfix changesets</li> <li><a href="https://github.com/mermaid-js/mermaid/commit/e81f31ffd6d995be902601b3eb171918d26f7d66"><code>e81f31f</code></a> docs: remove local-editor changeset</li> <li><a href="https://github.com/mermaid-js/mermaid/commit/7223f03c7318863c168e79e3f316229458a6afe7"><code>7223f03</code></a> Minor correction</li> <li>Additional commits viewable in <a href="https://github.com/mermaid-js/mermaid/compare/mermaid@11.12.3...mermaid@11.16.0">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
d2fa57ab98 |
build(deps): bump sharp from 0.34.5 to 0.35.2 (#8739)
Bumps [sharp](https://github.com/lovell/sharp) from 0.34.5 to 0.35.2. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/lovell/sharp/releases">sharp's releases</a>.</em></p> <blockquote> <h2>v0.35.2</h2> <ul> <li> <p>TypeScript: Add <code>mediaType</code> to metadata response. <a href="https://redirect.github.com/lovell/sharp/issues/4492">#4492</a></p> </li> <li> <p>Improve WebAssembly fallback detection. <a href="https://redirect.github.com/lovell/sharp/issues/4513">#4513</a></p> </li> <li> <p>Improve code bundler support with stub binaries. <a href="https://redirect.github.com/lovell/sharp/issues/4543">#4543</a></p> </li> <li> <p>Verify GIF <code>effort</code> option is an integer. <a href="https://redirect.github.com/lovell/sharp/pull/4544">#4544</a> <a href="https://github.com/metsw24-max"><code>@metsw24-max</code></a></p> </li> <li> <p>Verify <code>recomb</code> matrix entries are numbers. <a href="https://redirect.github.com/lovell/sharp/pull/4545">#4545</a> <a href="https://github.com/metsw24-max"><code>@metsw24-max</code></a></p> </li> <li> <p>TypeScript: Replace namespace with named exports for ESM. <a href="https://redirect.github.com/lovell/sharp/issues/4546">#4546</a></p> </li> <li> <p>Bound dilate and erode width to avoid mask-size overflow. <a href="https://redirect.github.com/lovell/sharp/pull/4548">#4548</a> <a href="https://github.com/metsw24-max"><code>@metsw24-max</code></a></p> </li> <li> <p>Verify <code>convolve</code> kernel values are numbers. <a href="https://redirect.github.com/lovell/sharp/pull/4549">#4549</a> <a href="https://github.com/metsw24-max"><code>@metsw24-max</code></a></p> </li> </ul> <h2>v0.35.2-rc.2</h2> <ul> <li> <p>TypeScript: Add <code>mediaType</code> to metadata response. <a href="https://redirect.github.com/lovell/sharp/issues/4492">#4492</a></p> </li> <li> <p>Improve WebAssembly fallback detection. <a href="https://redirect.github.com/lovell/sharp/issues/4513">#4513</a></p> </li> <li> <p>Improve code bundler support with stub binaries. <a href="https://redirect.github.com/lovell/sharp/issues/4543">#4543</a></p> </li> <li> <p>Verify GIF <code>effort</code> option is an integer. <a href="https://redirect.github.com/lovell/sharp/pull/4544">#4544</a> <a href="https://github.com/metsw24-max"><code>@metsw24-max</code></a></p> </li> <li> <p>Verify <code>recomb</code> matrix entries are numbers. <a href="https://redirect.github.com/lovell/sharp/pull/4545">#4545</a> <a href="https://github.com/metsw24-max"><code>@metsw24-max</code></a></p> </li> <li> <p>TypeScript: Replace namespace with named exports for ESM. <a href="https://redirect.github.com/lovell/sharp/issues/4546">#4546</a></p> </li> </ul> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/lovell/sharp/commit/c9622a38edfc6fc709764152ea34332ba01619cf"><code>c9622a3</code></a> Release v0.35.2</li> <li><a href="https://github.com/lovell/sharp/commit/cd4568fd41e576345be3c5f774d22e441ac563ac"><code>cd4568f</code></a> Upgrade to sharp-libvips v1.3.1</li> <li><a href="https://github.com/lovell/sharp/commit/78390cf3d22a79c799727564eb1d0ff92d0e759b"><code>78390cf</code></a> Tests: Add font file to prevent font discovery flakiness (<a href="https://redirect.github.com/lovell/sharp/issues/4550">#4550</a>)</li> <li><a href="https://github.com/lovell/sharp/commit/61210b4d0a6972e83fa5a8cef47e04445114c1e1"><code>61210b4</code></a> Verify convolve kernel values are numbers (<a href="https://redirect.github.com/lovell/sharp/issues/4549">#4549</a>)</li> <li><a href="https://github.com/lovell/sharp/commit/1cb27dcca43d2bb3b43fad485d9d54ece0ee1f3e"><code>1cb27dc</code></a> Prerelease v0.35.2-rc.2</li> <li><a href="https://github.com/lovell/sharp/commit/c7606c3ca7d8364d36984f44bb81a45c4b7733fb"><code>c7606c3</code></a> Upgrade to sharp-libvips v1.3.1-rc.0</li> <li><a href="https://github.com/lovell/sharp/commit/29d1e9e4d318775590e332f95088cf7f741c8dca"><code>29d1e9e</code></a> Prerelease v0.35.2-rc.1</li> <li><a href="https://github.com/lovell/sharp/commit/bbba0a16bab7a6cc2b6f3023f3dc0337336b39bd"><code>bbba0a1</code></a> Improve code bundler support with stub binaries</li> <li><a href="https://github.com/lovell/sharp/commit/ab528662ea949f60421dc527640d3188894fb57f"><code>ab52866</code></a> Bound dilate and erode width to avoid mask-size overflow (<a href="https://redirect.github.com/lovell/sharp/issues/4548">#4548</a>)</li> <li><a href="https://github.com/lovell/sharp/commit/0f594dde40ed08c391810da38d994e923fcdfc24"><code>0f594dd</code></a> Prerelease v0.35.2-rc.0</li> <li>Additional commits viewable in <a href="https://github.com/lovell/sharp/compare/v0.34.5...v0.35.2">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
29a26cbd65 |
build(deps): bump @codemirror/state from 6.5.4 to 6.7.0 (#8736)
Bumps [@codemirror/state](https://github.com/codemirror/state) from 6.5.4 to 6.7.0. <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/codemirror/state/blob/main/CHANGELOG.md">@codemirror/state's changelog</a>.</em></p> <blockquote> <h2>6.6.0 (2026-03-12)</h2> <h3>New features</h3> <p><code>EditorSelection.range</code> now takes an optional <code>assoc</code> argument.</p> <p><code>SelectionRange.extend</code> can now be given a third argument to specify associativity.</p> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li>See full diff in <a href="https://github.com/codemirror/state/commits">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
63aef57d49 |
build(deps): bump dotenv from 17.3.1 to 17.4.2 (#8737)
Bumps [dotenv](https://github.com/motdotla/dotenv) from 17.3.1 to 17.4.2. <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/motdotla/dotenv/blob/master/CHANGELOG.md">dotenv's changelog</a>.</em></p> <blockquote> <h2><a href="https://github.com/motdotla/dotenv/compare/v17.4.1...v17.4.2">17.4.2</a> (2026-04-12)</h2> <h3>Changed</h3> <ul> <li>Improved skill files - tightened up details (<a href="https://redirect.github.com/motdotla/dotenv/pull/1009">#1009</a>)</li> </ul> <h2><a href="https://github.com/motdotla/dotenv/compare/v17.4.0...v17.4.1">17.4.1</a> (2026-04-05)</h2> <h3>Changed</h3> <ul> <li>Change text <code>injecting</code> to <code>injected</code> (<a href="https://redirect.github.com/motdotla/dotenv/pull/1005">#1005</a>)</li> </ul> <h2><a href="https://github.com/motdotla/dotenv/compare/v17.3.1...v17.4.0">17.4.0</a> (2026-04-01)</h2> <h3>Added</h3> <ul> <li>Add <code>skills/</code> folder with focused agent skills: <code>skills/dotenv/SKILL.md</code> (core usage) and <code>skills/dotenvx/SKILL.md</code> (encryption, multiple environments, variable expansion) for AI coding agent discovery via the skills.sh ecosystem (<code>npx skills add motdotla/dotenv</code>)</li> </ul> <h3>Changed</h3> <ul> <li>Tighten up logs: <code>◇ injecting env (14) from .env</code> (<a href="https://redirect.github.com/motdotla/dotenv/pull/1003">#1003</a>)</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/motdotla/dotenv/commit/f116f70310abab44fbfddbaeb833698b5bf84a9b"><code>f116f70</code></a> 17.4.2</li> <li><a href="https://github.com/motdotla/dotenv/commit/3a8161274fdd745239b86e604f4a7e972a1d3902"><code>3a81612</code></a> fix visual order of faq</li> <li><a href="https://github.com/motdotla/dotenv/commit/13f55a89e136b2024e68d277b836dd5260fc16cf"><code>13f55a8</code></a> Merge branch 'skill'</li> <li><a href="https://github.com/motdotla/dotenv/commit/4bbbf73f0906bd69975c48bf310a84b686e5b1b4"><code>4bbbf73</code></a> reorganize faq</li> <li><a href="https://github.com/motdotla/dotenv/commit/c3da64bb2ba1d0e02f8b9b2b7ccb7e6f7a51d56c"><code>c3da64b</code></a> Merge pull request <a href="https://redirect.github.com/motdotla/dotenv/issues/1009">#1009</a> from motdotla/skill</li> <li><a href="https://github.com/motdotla/dotenv/commit/6f743b173fbd6c26f7eab7040d251f9a6c8b977d"><code>6f743b1</code></a> update source</li> <li><a href="https://github.com/motdotla/dotenv/commit/fc2c6247e858a32d4024cb06a5b0c79aa35851f5"><code>fc2c624</code></a> update skill</li> <li><a href="https://github.com/motdotla/dotenv/commit/972315ba74bb2bbba4483d112e853fd26006ef8a"><code>972315b</code></a> Tighten up skill</li> <li><a href="https://github.com/motdotla/dotenv/commit/2795fce3d1ed07b4c570f1e06ab1c0d533c86997"><code>2795fce</code></a> reorganize faq</li> <li><a href="https://github.com/motdotla/dotenv/commit/d5495d4ae8e4e41ef9a682c9e00c81552794274e"><code>d5495d4</code></a> adjust skill</li> <li>Additional commits viewable in <a href="https://github.com/motdotla/dotenv/compare/v17.3.1...v17.4.2">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
01f49b1fa0 |
build(deps): bump @aws-sdk/client-s3 from 3.1072.0 to 3.1075.0 (#8742)
Bumps [@aws-sdk/client-s3](https://github.com/aws/aws-sdk-js-v3/tree/HEAD/clients/client-s3) from 3.1072.0 to 3.1075.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/aws/aws-sdk-js-v3/releases">@aws-sdk/client-s3's releases</a>.</em></p> <blockquote> <h2>v3.1075.0</h2> <h4>3.1075.0(2026-06-23)</h4> <h5>New Features</h5> <ul> <li><strong>client-kafka:</strong> Amazon MSK Replicator now supports mTLS authentication when connecting to external Apache Kafka clusters, enabling customers to replicate data from clusters that require mutual TLS for client authentication. This capability is supported when replicating to Amazon MSK Express brokers. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/005f9529d4d3cd0c98b002a3584773b253a702dc">005f9529</a>)</li> </ul> <hr /> <p>For list of updated packages, view <strong>updated-packages.md</strong> in <strong>assets-3.1075.0.zip</strong></p> <h2>v3.1074.0</h2> <h4>3.1074.0(2026-06-22)</h4> <h5>Chores</h5> <ul> <li><strong>xml-builder:</strong> <ul> <li>move testing devDeps to root, remove unused nodable dep (<a href="https://redirect.github.com/aws/aws-sdk-js-v3/pull/8118">#8118</a>) (<a href="https://github.com/aws/aws-sdk-js-v3/commit/ed82880d26cac439d808eca5760da899cf449899">ed82880d</a>)</li> <li>parse XML internally (<a href="https://redirect.github.com/aws/aws-sdk-js-v3/pull/7863">#7863</a>) (<a href="https://github.com/aws/aws-sdk-js-v3/commit/74d0a071437c84a14396dbcc7f07f8480c369c58">74d0a071</a>)</li> </ul> </li> </ul> <h5>Documentation Changes</h5> <ul> <li>typo in contributing.md (<a href="https://redirect.github.com/aws/aws-sdk-js-v3/pull/8116">#8116</a>) (<a href="https://github.com/aws/aws-sdk-js-v3/commit/87ff33d30edb476912301f87ed6e2afac3cd5a93">87ff33d3</a>)</li> </ul> <h5>New Features</h5> <ul> <li><strong>clients:</strong> update client endpoints as of 2026-06-22 (<a href="https://github.com/aws/aws-sdk-js-v3/commit/3a55a3338792f712baf2e97d3f3c597fc28707c1">3a55a333</a>)</li> <li><strong>client-cloudwatch-logs:</strong> CloudWatch Logs Updates - New APIs introduced to support syslog ingestion to a log group. For more information, see CloudWatch Logs API documentation. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/01a3b513503169fb86db0bea0889f585c9004b55">01a3b513</a>)</li> <li><strong>client-bedrock-agentcore:</strong> Adds an optional extractionMode field to CreateEvent. SKIP retains the event in short-term memory but excludes it from long-term memory extraction. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/749753adae395e3ab3ab494df119f8d6354ca562">749753ad</a>)</li> <li><strong>client-omics:</strong> Adds support for scratch ephemeral storage mounted at tmp (<a href="https://github.com/aws/aws-sdk-js-v3/commit/331e3023c1049c5188dc4cec3adabae0c62e84f2">331e3023</a>)</li> <li><strong>client-application-signals:</strong> Application Signals now supports dynamic instrumentation and Service Events telemetry. Add instrumentation at runtime without restarts, and use fine-grained profiling data to quickly pinpoint latency and error root causes. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/f93b1c0333846b2d16c698f8c9b4034f93ab867c">f93b1c03</a>)</li> <li><strong>client-mediaconnect:</strong> AWS MediaConnect now supports Content Quality Analysis for Router Inputs, enabling detection of black frames, frozen frames, and silent audio with configurable thresholds. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/05054853a5aa6e740597c3932b5e2491b15e3a12">05054853</a>)</li> <li><strong>client-lambda-core:</strong> Initial release of the AWS Lambda Core SDK with APIs to create, manage, and tag network connectors that enable Lambda compute resources to access private resources in your Amazon VPC. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/e35cdab89fcf7ca679f37776418cb8d8e1269c14">e35cdab8</a>)</li> <li><strong>client-lambda:</strong> Add support for tagging Network Connector resources in AWS Lambda. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/fbfc40785e024fe2564e4be02ef425280693fce6">fbfc4078</a>)</li> <li><strong>client-guardduty:</strong> Added AI-powered investigations that automatically analyze security findings, correlate related activity, and produce structured summaries with risk assessment, confidence scoring, MITRE technique classification, and actionable next steps. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/83c2983945db4a54b004feed8d2d18935a3df431">83c29839</a>)</li> <li><strong>client-lambda-microvms:</strong> Lambda MicroVMs GA launch. Lambda MicroVMs enable isolated and highly responsive execution of user-supplied or LLM-generated code. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/5519a7e28fae4f57dd852109244b6370ff79f8bb">5519a7e2</a>)</li> <li><strong>client-kafka:</strong> Amazon MSK Replicator now supports mTLS authentication when connecting to external Apache Kafka clusters, enabling customers to replicate data from clusters that require mutual TLS for client authentication. This capability is supported when replicating to Amazon MSK Express brokers. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/ce7d1bf501fe6f7d6a454f96c1befc3829e23385">ce7d1bf5</a>)</li> <li><strong>client-quicksight:</strong> Updated the Amazon Quick Spaces API to remove unsupported SPACE and ARTIFACT values from the SpaceQuickSightResourceType enum. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/e1b325d42e491ceb75742bbdb56bfc3b98767ff1">e1b325d4</a>)</li> <li><strong>client-ec2:</strong> This release adds support for AMI Watermark and Allowed AMIs integration (<a href="https://github.com/aws/aws-sdk-js-v3/commit/d1698bed3961295343fdd86d0a57820538023bc7">d1698bed</a>)</li> <li><strong>client-direct-connect:</strong> Added VIF rate limiting support for AWS Direct Connect, allowing customers to set bandwidth allocations on virtual interfaces to manage traffic on dedicated connections. (<a href="https://github.com/aws/aws-sdk-js-v3/commit/228a95dc0c11cbcc1f007718faf93181c014a854">228a95dc</a>)</li> </ul> <h5>Bug Fixes</h5> <ul> <li><strong>cloudfront-signer:</strong> filename asterisk apostrophe encoding fix (<a href="https://redirect.github.com/aws/aws-sdk-js-v3/pull/8119">#8119</a>) (<a href="https://github.com/aws/aws-sdk-js-v3/commit/35acab408b9bd5350928525c8a67563ae551580a">35acab40</a>)</li> </ul> <hr /> <p>For list of updated packages, view <strong>updated-packages.md</strong> in <strong>assets-3.1074.0.zip</strong></p> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/aws/aws-sdk-js-v3/blob/main/clients/client-s3/CHANGELOG.md">@aws-sdk/client-s3's changelog</a>.</em></p> <blockquote> <h1><a href="https://github.com/aws/aws-sdk-js-v3/compare/v3.1074.0...v3.1075.0">3.1075.0</a> (2026-06-23)</h1> <p><strong>Note:</strong> Version bump only for package <code>@aws-sdk/client-s3</code></p> <h1><a href="https://github.com/aws/aws-sdk-js-v3/compare/v3.1073.0...v3.1074.0">3.1074.0</a> (2026-06-22)</h1> <p><strong>Note:</strong> Version bump only for package <code>@aws-sdk/client-s3</code></p> <h1><a href="https://github.com/aws/aws-sdk-js-v3/compare/v3.1072.0...v3.1073.0">3.1073.0</a> (2026-06-19)</h1> <p><strong>Note:</strong> Version bump only for package <code>@aws-sdk/client-s3</code></p> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/aws/aws-sdk-js-v3/commit/29ee1999340b8d8288184076df6557541974b13f"><code>29ee199</code></a> Publish v3.1075.0</li> <li><a href="https://github.com/aws/aws-sdk-js-v3/commit/c48dfa08aa057f100c69ccb571d35004eddec207"><code>c48dfa0</code></a> Publish v3.1074.0</li> <li><a href="https://github.com/aws/aws-sdk-js-v3/commit/74d0a071437c84a14396dbcc7f07f8480c369c58"><code>74d0a07</code></a> chore(xml-builder): parse XML internally (<a href="https://github.com/aws/aws-sdk-js-v3/tree/HEAD/clients/client-s3/issues/7863">#7863</a>)</li> <li><a href="https://github.com/aws/aws-sdk-js-v3/commit/ee71adc9663fc2ebaabae455981fd169fd6e97b2"><code>ee71adc</code></a> Publish v3.1073.0</li> <li>See full diff in <a href="https://github.com/aws/aws-sdk-js-v3/commits/v3.1075.0/clients/client-s3">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
dependabot[bot]
|
1b180fae1f |
build(deps): bump @agentclientprotocol/claude-agent-acp from 0.48.0 to 0.52.0 (#8745)
Bumps [@agentclientprotocol/claude-agent-acp](https://github.com/agentclientprotocol/claude-agent-acp) from 0.48.0 to 0.52.0. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/agentclientprotocol/claude-agent-acp/releases">@agentclientprotocol/claude-agent-acp's releases</a>.</em></p> <blockquote> <h2>v0.52.0</h2> <h2><a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.51.0...v0.52.0">0.52.0</a> (2026-06-25)</h2> <h3>Features</h3> <ul> <li>Add version flag handling (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/813">#813</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/9616bdac47505e4a14c36d667fcffc9ae97e1f2a">9616bda</a>), closes <a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/809">#809</a></li> <li><strong>deps-dev:</strong> bump expect-type from 1.3.0 to 1.4.0 in the minor group (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/814">#814</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/61272acb30dcafaa2455d334b11ce2ad97339707">61272ac</a>)</li> <li><strong>deps:</strong> Update <code>@anthropic-ai/claude-agent-sdk</code> to 0.3.191 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/810">#810</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/228f02ecfb23be16e59e121c6b42c0f2b2f40a4e">228f02e</a>)</li> <li>Push session title updates at turn end (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/812">#812</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/1fe7ec09a3a7bcb7501231dae4b0ffe6ef9b70a4">1fe7ec0</a>)</li> </ul> <h2>v0.51.0</h2> <h2><a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.50.0...v0.51.0">0.51.0</a> (2026-06-24)</h2> <h3>Features</h3> <ul> <li><strong>deps:</strong> bump the minor group with 11 updates (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/807">#807</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/8f6ebd1d9198edf723f4c8c1aa2b49b906c46646">8f6ebd1</a>)</li> </ul> <h2>v0.50.0</h2> <h2><a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.49.0...v0.50.0">0.50.0</a> (2026-06-23)</h2> <h3>Features</h3> <ul> <li><strong>acp:</strong> Handle ACP request cancellation signals (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/801">#801</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/9013d1d46883a7f3774a63a9dca16c4a0f634a97">9013d1d</a>)</li> <li><strong>deps:</strong> bump actions/checkout from 6.0.3 to 7.0.0 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/803">#803</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/044c43e0c894082b9e747c01e9dbde6e21036823">044c43e</a>)</li> <li><strong>deps:</strong> upgrade to <code>@anthropic-ai/claude-agent-sdk</code><a href="https://github.com/0"><code>@0</code></a>.3.186 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/806">#806</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/a7e6137f6877b72b8daa39e74971c3559db8d28f">a7e6137</a>)</li> </ul> <h2>v0.49.0</h2> <h2><a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.48.0...v0.49.0">0.49.0</a> (2026-06-22)</h2> <h3>Features</h3> <ul> <li>Update to claude-agent-sdk 0.3.185 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/798">#798</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/8dc8c864263fa50d03bec7ebff7aee776604cb3d">8dc8c86</a>)</li> </ul> <h3>Bug Fixes</h3> <ul> <li>Deduplicate streamed assistant blocks by content (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/800">#800</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/960f62d76582ae5c9c5575ab66974809049ce1d0">960f62d</a>)</li> <li>Infer 1M context from model descriptions (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/799">#799</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/508453c288b4a12701abd507199e7fa0ab172171">508453c</a>)</li> </ul> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/agentclientprotocol/claude-agent-acp/blob/main/CHANGELOG.md">@agentclientprotocol/claude-agent-acp's changelog</a>.</em></p> <blockquote> <h2><a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.51.0...v0.52.0">0.52.0</a> (2026-06-25)</h2> <h3>Features</h3> <ul> <li>Add version flag handling (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/813">#813</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/9616bdac47505e4a14c36d667fcffc9ae97e1f2a">9616bda</a>), closes <a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/809">#809</a></li> <li><strong>deps-dev:</strong> bump expect-type from 1.3.0 to 1.4.0 in the minor group (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/814">#814</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/61272acb30dcafaa2455d334b11ce2ad97339707">61272ac</a>)</li> <li><strong>deps:</strong> Update <code>@anthropic-ai/claude-agent-sdk</code> to 0.3.191 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/810">#810</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/228f02ecfb23be16e59e121c6b42c0f2b2f40a4e">228f02e</a>)</li> <li>Push session title updates at turn end (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/812">#812</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/1fe7ec09a3a7bcb7501231dae4b0ffe6ef9b70a4">1fe7ec0</a>)</li> </ul> <h2><a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.50.0...v0.51.0">0.51.0</a> (2026-06-24)</h2> <h3>Features</h3> <ul> <li><strong>deps:</strong> bump the minor group with 11 updates (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/807">#807</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/8f6ebd1d9198edf723f4c8c1aa2b49b906c46646">8f6ebd1</a>)</li> </ul> <h2><a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.49.0...v0.50.0">0.50.0</a> (2026-06-23)</h2> <h3>Features</h3> <ul> <li><strong>acp:</strong> Handle ACP request cancellation signals (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/801">#801</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/9013d1d46883a7f3774a63a9dca16c4a0f634a97">9013d1d</a>)</li> <li><strong>deps:</strong> bump actions/checkout from 6.0.3 to 7.0.0 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/803">#803</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/044c43e0c894082b9e747c01e9dbde6e21036823">044c43e</a>)</li> <li><strong>deps:</strong> upgrade to <code>@anthropic-ai/claude-agent-sdk</code><a href="https://github.com/0"><code>@0</code></a>.3.186 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/806">#806</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/a7e6137f6877b72b8daa39e74971c3559db8d28f">a7e6137</a>)</li> </ul> <h2><a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.48.0...v0.49.0">0.49.0</a> (2026-06-22)</h2> <h3>Features</h3> <ul> <li>Update to claude-agent-sdk 0.3.185 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/798">#798</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/8dc8c864263fa50d03bec7ebff7aee776604cb3d">8dc8c86</a>)</li> </ul> <h3>Bug Fixes</h3> <ul> <li>Deduplicate streamed assistant blocks by content (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/800">#800</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/960f62d76582ae5c9c5575ab66974809049ce1d0">960f62d</a>)</li> <li>Infer 1M context from model descriptions (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/799">#799</a>) (<a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/508453c288b4a12701abd507199e7fa0ab172171">508453c</a>)</li> </ul> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/e9163f855398511c6eec0116216d8c06c52ec658"><code>e9163f8</code></a> chore(main): release 0.52.0 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/811">#811</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/61272acb30dcafaa2455d334b11ce2ad97339707"><code>61272ac</code></a> feat(deps-dev): bump expect-type from 1.3.0 to 1.4.0 in the minor group (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/814">#814</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/9616bdac47505e4a14c36d667fcffc9ae97e1f2a"><code>9616bda</code></a> feat: Add version flag handling (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/813">#813</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/1fe7ec09a3a7bcb7501231dae4b0ffe6ef9b70a4"><code>1fe7ec0</code></a> feat: Push session title updates at turn end (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/812">#812</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/228f02ecfb23be16e59e121c6b42c0f2b2f40a4e"><code>228f02e</code></a> feat(deps): Update <code>@anthropic-ai/claude-agent-sdk</code> to 0.3.191 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/810">#810</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/23626c9a43b4fa2b4e98cf1abb25c55985711075"><code>23626c9</code></a> chore(main): release 0.51.0 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/808">#808</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/8f6ebd1d9198edf723f4c8c1aa2b49b906c46646"><code>8f6ebd1</code></a> feat(deps): bump the minor group with 11 updates (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/807">#807</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/07911601ccd2b8d8628aed545f7715c6aa0fa429"><code>0791160</code></a> chore(main): release 0.50.0 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/802">#802</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/a7e6137f6877b72b8daa39e74971c3559db8d28f"><code>a7e6137</code></a> feat(deps): upgrade to <code>@anthropic-ai/claude-agent-sdk</code><a href="https://github.com/0"><code>@0</code></a>.3.186 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/806">#806</a>)</li> <li><a href="https://github.com/agentclientprotocol/claude-agent-acp/commit/044c43e0c894082b9e747c01e9dbde6e21036823"><code>044c43e</code></a> feat(deps): bump actions/checkout from 6.0.3 to 7.0.0 (<a href="https://redirect.github.com/agentclientprotocol/claude-agent-acp/issues/803">#803</a>)</li> <li>Additional commits viewable in <a href="https://github.com/agentclientprotocol/claude-agent-acp/compare/v0.48.0...v0.52.0">compare view</a></li> </ul> </details> <br /> [](https://docs.github.com/en/github/managing-security-vulnerabilities/about-dependabot-security-updates#about-compatibility-scores) Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting `@dependabot rebase`. [//]: # (dependabot-automerge-start) [//]: # (dependabot-automerge-end) --- <details> <summary>Dependabot commands and options</summary> <br /> You can trigger Dependabot actions by commenting on this PR: - `@dependabot rebase` will rebase this PR - `@dependabot recreate` will recreate this PR, overwriting any edits that have been made to it - `@dependabot show <dependency name> ignore conditions` will show all of the ignore conditions of the specified dependency - `@dependabot ignore this major version` will close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this minor version` will close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself) - `@dependabot ignore this dependency` will close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself) </details> Signed-off-by: dependabot[bot] <support@github.com> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com> |
||
|
Devin FoleyandPaperclip
|
8d9f9fd240 |
Add reusable sandbox custom images (#8794)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work.
> - A growing part of that work runs in sandboxed environments rather
than on the operator's local machine.
> - Today sandbox providers can start fresh workspaces and run probes,
but they do not have a shared contract for capturing and reusing
prepared sandbox state.
> - Operators need a way to set up tools, credentials, and project
dependencies once, then reuse that prepared image for later agent runs.
> - This pull request adds reusable sandbox custom images across the
provider contract, server runtime, and board UI.
> - It also keeps probes and sandbox copy flows aligned with
pre-authenticated/custom-image environments.
> - The benefit is faster, more reliable sandbox runs without repeatedly
rebuilding the same environment setup.

## Linked Issues or Issue Description

No public GitHub issue was found for this change. Inline feature request
follows.

### Problem or motivation

Sandboxed agents need reusable prepared runtime state so repeated runs
do not require manual setup every time. Operators often need system
packages, CLIs, SDKs, dependency caches, credentials, and project
tooling available before an agent can work productively.

### Proposed solution

Add a provider-level custom-image capability, server-side setup/capture
lifecycle, Daytona/fake provider support, and board UI controls for
creating, testing, selecting, and deleting custom images.

### Alternatives considered

Leaving this as provider-specific setup outside Paperclip would keep the
control plane blind to image state and would not give agents consistent
environment metadata. Re-running setup commands for every lease is
simpler, but slower and less reliable for interactive or credentialed
setup.

### Roadmap alignment

Checked `ROADMAP.md`; this aligns with the Cloud / Sandbox agents
roadmap area and does not duplicate any related public issue or PR found
by search.

Additional context:
- Subsystem affected: cross-cutting (`packages/db`, `packages/shared`,
`packages/plugins`, `server`, `ui`).
- Duplicate search: searched GitHub for `sandbox custom image` and
`sandbox template environment`; no related public issues or PRs were
found.

## What Changed

- Added custom-image shared types, validators, constants, API paths, and
database schema/migration.
- Added server services/routes for custom-image templates and setup
sessions, including runtime cleanup and provider metadata handling.
- Extended plugin/sandbox provider capabilities for interactive setup,
template capture, and template deletion.
- Implemented custom-image support in the fake sandbox provider and
Daytona provider.
- Updated environment runtime/config handling so active custom images
flow into leases, probes, and agent execution.
- Added board UI controls and API client support for custom-image setup,
capture, selection, status, and error states.
- Hardened sandbox copy/probe behavior for insecure clipboard contexts
and pre-authenticated sandbox images.
- Added targeted coverage across shared validators, DB schema, server
routes/services, provider plugins, adapter probes, and UI flows.

## Verification

- `pnpm install --frozen-lockfile --ignore-scripts`
- `pnpm vitest run
packages/adapters/claude-local/src/server/test.probe.test.ts
packages/adapters/claude-local/src/server/test.ts
packages/adapters/codex-local/src/server/test.remote.test.ts
packages/adapters/codex-local/src/server/test.ts`
- `pnpm --filter @paperclipai/adapter-claude-local typecheck`
- `pnpm --filter @paperclipai/adapter-codex-local typecheck`
- `pnpm vitest run
packages/db/src/environment-custom-images-schema.test.ts
packages/shared/src/environment-custom-images.test.ts
packages/shared/src/validators/plugin.test.ts
server/src/__tests__/environment-custom-images-service.test.ts
server/src/__tests__/workspace-runtime.test.ts
packages/plugins/sandbox-providers/daytona/src/plugin.test.ts
ui/src/pages/CompanyEnvironments.test.tsx
ui/src/pages/CompanySettings.test.tsx`
- `pnpm -r typecheck`
- `pnpm build`
- `rm -rf packages/db/dist && pnpm test:run`
- Public-safety scan of the final diff found no internal Paperclip issue
links, private instance URLs, or real secret patterns.

## Risks

- Adds a database migration and new environment runtime tables, so
migration ordering and rollback need care.
- Provider implementations may differ in how reliably they can
capture/delete images; unsupported providers surface capability-gated UI
states.
- Custom-image state can contain operator-prepared tooling and
credentials inside the provider image, so providers must enforce their
own access controls and cleanup semantics.
- Broad surface area across shared contracts, server runtime, plugins,
adapters, and UI means CI and Greptile review should be watched closely.

> For core feature work, check [`ROADMAP.md`](ROADMAP.md) first and
discuss it in `#dev` before opening the PR. Feature PRs that overlap
with planned core work may need to be redirected — check the roadmap
first. See `CONTRIBUTING.md`.

## Model Used

OpenAI GPT-5 (`gpt-5`) via Codex CLI with tool use and code execution.
Assisted with branch cleanup, conflict resolution, local verification,
and PR preparation. Earlier branch implementation work was assisted by
Paperclip-managed Claude/Codex agents.

## Checklist

- [x] I have included a thinking path that traces from project context
to this change
- [x] I have specified the model used (with version and capability
details)
- [x] I have checked ROADMAP.md and confirmed this PR does not duplicate
planned core work
- [x] I have searched GitHub for duplicate or related PRs and linked
them above
- [x] I have either (a) linked existing issues with `Fixes: #` / `Closes
#` / `Refs #` OR (b) described the issue in-PR following the relevant
issue template
- [x] I have not referenced internal/instance-local Paperclip issues or
links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip`
URLs)
- [x] My branch name describes the change (e.g. `docs/...`, `fix/...`)
and contains no internal Paperclip ticket id or instance-derived details
- [x] I have run tests locally and they pass
- [x] I have added or updated tests where applicable
- [x] I have updated relevant documentation to reflect my changes
- [x] I have considered and documented any risks above
- [ ] All Paperclip CI gates are green
- [ ] Greptile is 5/5 with no open P2s, recommendations, or follow-ups
- [x] I will address all Greptile and reviewer comments before
requesting merge

---------

Co-authored-by: Paperclip <noreply@paperclip.ing>
canary/v2026.630.0-canary.5 |
||
|
Devin Foley
|
b61c2852fb |
build(ui): drop redundant tsc type-check from ui build (#8781)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work
> - CI runs a set of required PR checks; the Canary Dry Run job is the
slowest (~4m)
> - Its dominant cost is `release.sh` Step 2 `pnpm build` (~133s), whose
critical path is the `ui` package
> - In `ui`, `tsc -b` runs ~46s *before* `vite build` (~20s), but
`ui/tsconfig.json` sets `noEmit: true`, so `tsc -b` is a pure type-check
that emits nothing — vite produces all artifacts
> - The PR workflow already runs a parallel Typecheck job
(`typecheck:build-gaps`) that auto-type-checks any workspace package
whose build script omits `tsc`
> - This pull request drops `tsc -b` from the `ui` build so the
type-check moves off the build/release critical path onto the slack-rich
Typecheck job
> - The benefit is ~46s shaved off the slowest PR check with no loss of
type coverage

## What Changed

- `ui/package.json`: `build` script changed from `tsc -b && vite build`
to `vite build`.
- Type coverage is preserved automatically:
`scripts/run-typecheck-build-gaps.mjs` already type-checks any workspace
whose `build` script omits `tsc` and defines a `typecheck` script. With
this change, `@paperclipai/ui` (whose `typecheck` is `tsc -b`) is now
picked up by the parallel Typecheck job. No script edit was required —
the gap-detection is generic.

## Verification

- `pnpm --filter @paperclipai/ui build` produces `ui/dist` via vite
alone (no `tsc` invocation).
- `pnpm typecheck:build-gaps` now type-checks `@paperclipai/ui` and
exits 0.
- A type error in `ui` still fails the parallel Typecheck job, so
type-error coverage is unchanged.

## Risks

- Low. The type-check is relocated, not removed. This is build-tooling
only — no migration, no runtime behavior change. If
`scripts/run-typecheck-build-gaps.mjs` ever stopped covering `ui`, a
type error could slip past the build job — but its gap-detection is
generic (any package with a tsc-less build plus a `typecheck` script),
and `ui` qualifies.

## Model Used

Claude (Anthropic), `claude-opus-4` family, extended-thinking mode with
tool use, operating as an automated CI-health agent.
canary/v2026.630.0-canary.4 |
||
|
Devin FoleyandPaperclip
|
0c2ec7deb4 |
Fix sandboxed Claude and Codex probe behavior (#8775)
## Thinking Path > - Paperclip is the open source app people use to manage AI agents for work. > - Local adapters are the bridge between Paperclip's control plane and provider CLIs such as Claude Code and Codex. > - Those adapters can run either on the host machine or inside a remote/sandbox execution target. > - Sandbox probes need to validate the same auth/config path that real sandbox execution will use. > - The previous probe paths could surface misleading Claude errors, rely on host-only Codex state, or upload far more Codex home state than the probe needed. > - This pull request fixes the Claude and Codex sandbox probe/runtime behavior together while keeping provider-specific sandbox image work out of scope. > - The benefit is faster, clearer adapter health checks that better match real sandbox execution. ## Linked Issues or Issue Description No public GitHub issue was found for this exact bug during duplicate search. Bug report: **What happened?** Sandboxed Claude/Codex adapter tests could diverge from real runtime auth/config behavior. Claude sandbox probes could show the leading stream init line instead of the real final error, and Codex sandbox probes could upload full managed home state or mask a sandbox-local login with an empty uploaded `CODEX_HOME`. **Expected behavior** Sandbox probes should exercise the remote runtime contract, preserve useful sandbox credentials, avoid relying on unrelated host state, and report actionable probe failures. **Steps to reproduce** 1. Configure a remote/sandbox execution target for `claude_local` or `codex_local`. 2. Run the environment Test/probe path where host credentials differ from the sandbox's runtime credentials or the managed Codex home contains session history. 3. Observe that probe behavior can differ from the actual sandbox runtime path or surface an unhelpful Claude stream initialization line. **Paperclip version or commit** Current `master` before this PR, based on `4a2447da3`. **Deployment mode** Local development/control-plane deployment with remote sandbox execution targets. Related search performed: - Public issues: `Claude sandbox probe`, `Codex CODEX_HOME sandbox` returned no matches. - Public PRs: `Claude Codex sandbox probe`, `codex home sandbox`, `claude auth sandbox` returned no matches. ## What Changed - Made Claude sandbox Test probes materialize the same Paperclip-managed Claude config seed path used by sandbox execution. - Preserved sandbox-local Claude credentials when materializing remote Claude config and expanded auth-required detection for `/login` API-key failures. - Improved Claude hello-probe diagnostics so the final result/error is surfaced instead of the unhelpful stream init event, with transient upstream failures downgraded to warnings. - Changed Codex probe behavior to upload only minimal auth/config files instead of the full managed `CODEX_HOME`. - Let Codex sandbox probes leave `CODEX_HOME` unset when the host has no credentials, so pre-authenticated sandbox images can be tested directly. - Excluded bulky host-local Codex session/shell state from sandbox runtime home uploads. - Switched the Codex local default model away from the ChatGPT-unsupported `gpt-5.3-codex` option. - Added regression coverage for Claude parsing/probe paths, Codex adapter metadata/argument/probe behavior, and server-level Claude sandbox environment behavior. ## Verification Passed locally: - `pnpm install --frozen-lockfile` - `pnpm vitest run packages/adapters/claude-local/src/server/parse.test.ts packages/adapters/claude-local/src/server/test.probe.test.ts server/src/__tests__/claude-local-adapter-environment.test.ts` - `pnpm vitest run packages/adapters/codex-local/src/index.test.ts packages/adapters/codex-local/src/server/codex-args.test.ts packages/adapters/codex-local/src/server/test.remote.test.ts` - `pnpm --filter @paperclipai/adapter-claude-local typecheck` - `pnpm --filter @paperclipai/adapter-codex-local typecheck` - `pnpm --filter @paperclipai/server typecheck` - `git diff --check` ## Risks - Adapter configuration behavior is sensitive to local vs sandboxed execution mode, so review should focus on environment detection, argument construction, and any state written during probe/test runs. - The Codex default-model change may affect newly created agents that rely on the adapter default instead of an explicit model. - Excluding Codex session/shell state from sandbox uploads should be safe for fresh sandbox runs, but reviewers should confirm no runtime resume path depends on that host-local state. - Provider-specific setup/capture behavior is intentionally left to separate work. ## Model Used OpenAI GPT-5 Codex via Paperclip `codex_local`; tool-enabled local coding session with terminal access. Context window size was not exposed by the runtime. ## Checklist - [x] I have included a thinking path that traces from project context to this change - [x] I have specified the model used (with version and capability details) - [x] I have checked ROADMAP.md and confirmed this PR does not duplicate planned core work - [x] I have searched GitHub for duplicate or related PRs and linked them above - [x] I have either (a) linked existing issues with `Fixes: #` / `Closes #` / `Refs #` OR (b) described the issue in-PR following the relevant issue template - [x] I have not referenced internal/instance-local Paperclip issues or links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip` URLs) - [x] My branch name describes the change (e.g. `docs/...`, `fix/...`) and contains no internal Paperclip ticket id or instance-derived details - [x] I have run tests locally and they pass - [x] I have added or updated tests where applicable - [x] I have updated relevant documentation to reflect my changes - [x] I have considered and documented any risks above - [x] All Paperclip CI gates are green - [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups - [x] I will address all Greptile and reviewer comments before requesting merge --------- Co-authored-by: Paperclip <noreply@paperclip.ing> |
||
|
DottaandPaperclip
|
37c097a474 |
[codex] Update watchdog properties pane cache (#8786)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work.
> - The issue detail surface includes an Issue Properties pane that
shows live metadata for a selected issue.
> - Watchdog configuration can be changed from that pane, but cached
issue detail data also feeds the pane key and rerender behavior.
> - If the cache does not reflect watchdog changes immediately, the
properties pane can keep stale watchdog state until a later refetch
completes.
> - This pull request updates the watchdog save/delete paths to write
the returned watchdog state into cached issue detail data.
> - It also includes watchdog fields in the issue properties panel key
so watchdog configuration changes invalidate the memoized panel state.
> - The benefit is a properties pane that updates consistently after
operators set or remove a watchdog.

## Linked Issues or Issue Description

Refs #8789

This PR fixes stale watchdog state in the Issue Properties pane after
watchdog save/delete mutations.

## What Changed

- Write the saved watchdog summary into cached issue detail data after a
successful watchdog upsert using the exact
`queryKeys.issues.detail(issue.id)` key.
- Clear cached issue detail watchdog data after a successful watchdog
delete using the exact `queryKeys.issues.detail(issue.id)` key.
- Include stable watchdog fields in `buildIssuePropertiesPanelKey` so
watchdog configuration changes produce a new panel key.
- Add focused tests for watchdog cache updates and panel-key
invalidation, including save and delete cache assertions.

## Verification

- `pnpm --filter @paperclipai/ui exec vitest run
src/components/IssueProperties.test.tsx
src/lib/issue-properties-panel-key.test.ts`
- Result: 2 files passed, 40 tests passed.

## Risks

Low risk. The change is scoped to UI cache handling for issue detail
watchdog state and panel-key generation. The main risk is an unexpected
query-cache shape, covered by focused tests around the existing issue
detail query key.

> For core feature work, check [`ROADMAP.md`](ROADMAP.md) first and
discuss it in `#dev` before opening the PR. Feature PRs that overlap
with planned core work may need to be redirected — check the roadmap
first. See `CONTRIBUTING.md`.

## Model Used

OpenAI Codex coding agent running GPT-5-class model with repository tool
use and local command execution. The exact backend model identifier and
context window are not exposed in this runtime.

## Checklist

- [x] I have included a thinking path that traces from project context
to this change
- [x] I have specified the model used (with version and capability
details)
- [x] I have checked ROADMAP.md and confirmed this PR does not duplicate
planned core work
- [x] I have searched GitHub for duplicate or related PRs and linked
them above
- [x] I have either (a) linked existing issues with `Fixes: #` / `Closes
#` / `Refs #` OR (b) described the issue in-PR following the relevant
issue template
- [x] I have not referenced internal/instance-local Paperclip issues or
links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip`
URLs)
- [x] My branch name describes the change (e.g. `docs/...`, `fix/...`)
and contains no internal Paperclip ticket id or instance-derived details
- [x] I have run tests locally and they pass
- [x] I have added or updated tests where applicable
- [x] I have updated relevant documentation to reflect my changes
- [x] I have considered and documented any risks above
- [ ] All Paperclip CI gates are green
- [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups
- [x] I will address all Greptile and reviewer comments before
requesting merge

---------

Co-authored-by: Paperclip <noreply@paperclip.ing>
canary/v2026.630.0-canary.3 |