mirror of
https://github.com/paperclipai/paperclip.git
synced 2026-11-07 07:55:47 +01:00
afaad3e9ca9d8a5566a20d37ad5799bbf643dca8
5
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 Devin Foley |
5b6e54fba8 |
fix(cli): accept prompt defaults in onboarding wizard validators (#13520)
## Thinking Path

> - Paperclip is the open source app people use to manage AI agents for
work
> - The CLI onboarding wizard's custom-setup path collects server,
database, storage, and secrets configuration through `@clack/prompts`
text prompts, most of which show a sensible default
> - `@clack/prompts` runs each prompt's `validate` callback on the raw
typed value, and only substitutes `defaultValue` after validation passes
— so pressing Enter to accept a shown default hands the validator an
empty string
> - Eleven of the wizard's validators reject the empty string, which
makes their own displayed defaults unacceptable: accepting "Embedded
PostgreSQL port: 54329" fails with "Port must be an integer between 1
and 65535", "Backup directory" fails with "Backup directory is
required", and so on through every prompt in the custom path
> - This pull request makes each affected validator accept empty input
when a default exists, while keeping all real validation for typed input
> - The benefit is that the custom-setup wizard is walkable by pressing
Enter through the defaults, as the UI clearly intends

## Linked Issues or Issue Description

No existing issue. Description follows the bug-report template:

**What happened?**
In `paperclipai onboard` custom setup, pressing Enter to accept a
prompt's displayed default fails validation on eleven prompts. Confirmed
live on the "Embedded PostgreSQL port" prompt (default 54329 → "Port
must be an integer between 1 and 65535") and the "Backup directory"
prompt (populated default path → "Backup directory is required"). The
only way through is to retype every default by hand.

**Expected behavior**
Pressing Enter accepts the displayed default, as in every standard
`@clack/prompts` flow.

**Steps to reproduce**
1. `npx paperclipai onboard` → choose Custom setup.
2. At "Embedded PostgreSQL port", press Enter to accept the shown
default.
3. Validation rejects it. Same for the backup directory, backup
interval/retention, server port, bind host, storage directory, S3
bucket/region, and secrets key-file prompts.

**Paperclip version or commit**
Reproduced on `2026.915.0-canary.11`; the same validators exist in the
latest stable (`v2026.831.1`) — long-standing, not a recent regression.

**Deployment mode**
Any (the bug is in the CLI wizard).

**Installation method**
`npx paperclipai onboard`.

## What Changed

- Audited all 15 `validate:` callbacks across
`cli/src/prompts/{database,server,storage,llm,secrets}.ts`. Eleven
rejected the empty string while displaying a default; two were already
fine (hostname CSV prompts, where empty parses to `[]`); one is an
intentionally required password with no default (left alone); one
(PostgreSQL connection string) and one (public base URL) are
conditionally required — empty now passes only when a saved default
exists, so fresh setups still enforce the field
- Fix pattern: allow empty/undefined input at the top of each affected
validator; every check for non-empty typed input is unchanged. One
deliberate exception: the bind-host validator validates `(val ||
defaultHost)` so accepting the default still runs the loopback safety
check rather than bypassing it
- New `cli/src/__tests__/prompt-default-accept.test.ts` (repo-convention
vitest + clack mock reproducing real submit semantics — validate raw
`""`, then substitute the default): drives the four prompt modules
end-to-end and unit-exercises each captured validator (empty accepted,
garbage still rejected, required-when-fresh still rejected)

## Verification

- `pnpm exec vitest run src/__tests__/prompt-default-accept.test.ts` in
`cli/`: 13/13 pass; with the prompt fixes stashed: 12/13 fail — the
suite reproduces the bug
- Full cli suite: 483 passed; 15 failures are pre-existing/environmental
on the clean tree too (macOS `/var` realpath mismatch in
`worktree.test.ts`, one parallel-run flake that passes in isolation)
- `pnpm run typecheck` in `cli/`: zero errors in `cli/src` (the 228
pre-existing errors in `../server/src` from missing prebuilt workspace
dist are identical with and without the change)

## Risks

- Low. Typed input validates exactly as before; whitespace-only input is
still rejected (clack substitutes the default only for truly-empty
input). The two conditionally-required prompts still hard-require a
value on fresh setups
- No migrations, no API surface changes; CLI-only

## Model Used

Claude Fable 5 (`claude-fable-5`), extended thinking with tool use
(Claude Code); implementation drafted by a subagent on the same model
and reviewed before commit.

## Checklist

- [x] I have included a thinking path that traces from project context
to this change
- [x] I have specified the model used (with version and capability
details)
- [x] I have checked ROADMAP.md and confirmed this PR does not duplicate
planned core work
- [x] I have searched GitHub for duplicate or related PRs and linked
them above
- [x] I have either (a) linked existing issues with `Fixes: #` / `Closes
#` / `Refs #` OR (b) described the issue in-PR following the relevant
issue template
- [x] I have not referenced internal/instance-local Paperclip issues or
links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip`
URLs)
- [x] My branch name describes the change (e.g. `docs/...`, `fix/...`)
and contains no internal Paperclip ticket id or instance-derived details
- [x] I have run tests locally and they pass
- [x] I have added or updated tests where applicable
- [x] I have updated relevant documentation to reflect my changes
- [x] I have considered and documented any risks above
- [x] All Paperclip CI gates are green
- [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups
- [x] I will address all Greptile and reviewer comments before
requesting merge
|
||
|
|
778e775c35 |
Add secrets provider vaults and remote import (#5429)
## Thinking Path > - Paperclip orchestrates AI-agent companies and needs secrets handling to work across local development, hosted operators, and governed agent execution. > - The affected subsystem is the company-scoped secrets control plane: database schema, server services/routes, CLI workflows, and the Secrets settings UI. > - The gap was that secrets were local-only and operators could not manage provider vaults or import existing remote references without exposing plaintext. > - This branch adds provider vault configuration plus an AWS Secrets Manager remote-import path while preserving company boundaries, binding context, and audit trails. > - I kept the PR to a single branch PR, removed unrelated lockfile/package drift, rebased the full branch onto the current `public-gh/master`, and addressed fresh Greptile findings. > - The benefit is a reviewable implementation of provider-backed secrets with focused tests covering provider selection, import conflicts, deleted secret reuse, rotation guards, and AWS signing behavior. ## What Changed - Added provider vault support for company secrets, including provider config storage, default vault handling, health checks, binding usage, access events, and remote import preview/commit. - Added an AWS Secrets Manager provider using SigV4 request signing, bounded request timeouts, namespace guardrails, cached runtime credential resolution, and external-reference linking without plaintext reads. - Added Secrets UI surfaces for vault management and remote import, plus CLI/API documentation for setup and operations. - Stabilized routine webhook secret binding paths and SSH environment-driver fixture bindings discovered during verification. - Addressed Greptile and CI findings: no lockfile/package drift, monotonic migration metadata, disabled-vault default races, soft-deleted secret hiding/recreate behavior, remove behavior with disabled vaults, soft-deleted external-reference re-import, non-active rotation guards, managed-secret soft deletion through PATCH, and per-call AWS SDK credential client churn. - Rebased this branch onto `public-gh/master` at `0e1a5828` and force-pushed with lease to keep this as the single PR for the branch. ## Verification - `git fetch public-gh master` - `git rebase public-gh/master` - `git diff --name-only public-gh/master...HEAD | grep '^pnpm-lock\.yaml$' || true` confirmed `pnpm-lock.yaml` is not in the PR diff. - Confirmed migration ordering: master ends at `0081_optimal_dormammu`; this PR adds `0082_dry_vision` and `0083_company_secret_provider_configs`. - Inspected migrations for repeat safety: new tables/indexes use `IF NOT EXISTS`; foreign keys are guarded by `DO $$ ... IF NOT EXISTS`; column additions use `ADD COLUMN IF NOT EXISTS`. - `pnpm -r typecheck` passed before the Greptile follow-up commits. - `pnpm test:run` ran the full stable Vitest path before the Greptile follow-up commits; it completed with 3 timing-related failures under parallel load: `codex-local-execute.test.ts`, `cursor-local-execute.test.ts`, and `environment-service.test.ts`. - `pnpm --filter @paperclipai/server exec vitest run src/__tests__/codex-local-execute.test.ts src/__tests__/cursor-local-execute.test.ts src/__tests__/environment-service.test.ts` passed on targeted rerun (`24/24`). - `pnpm build` passed before the Greptile follow-up commits. Vite reported existing chunk-size/dynamic-import warnings. - After Greptile follow-up commits: `pnpm --filter @paperclipai/server exec vitest run src/__tests__/secrets-service.test.ts` passed (`26/26`). - After Greptile follow-up commits: `pnpm --filter @paperclipai/server exec vitest run src/__tests__/aws-secrets-manager-provider.test.ts src/__tests__/secrets-service.test.ts` passed (`39/39`). - After Greptile follow-up commits: `pnpm --filter @paperclipai/server typecheck` passed. - Captured Storybook screenshots from `ui/storybook-static` for visual review. - Latest PR checks on `5ca3a5cf`: `policy`, serialized server suites 1/4-4/4, `Canary Dry Run`, `e2e`, `security/snyk`, and `Greptile Review` pass; aggregate `verify` is still registering the completed child checks. - Greptile review loop continued through the latest requested pass; all Greptile review threads are resolved and the latest `Greptile Review` check on `5ca3a5cf` passed with 0 comments added. ## Screenshots Before: the provider-vault and remote-import surfaces did not exist on `master`; these are after-state screenshots from the Storybook fixtures. 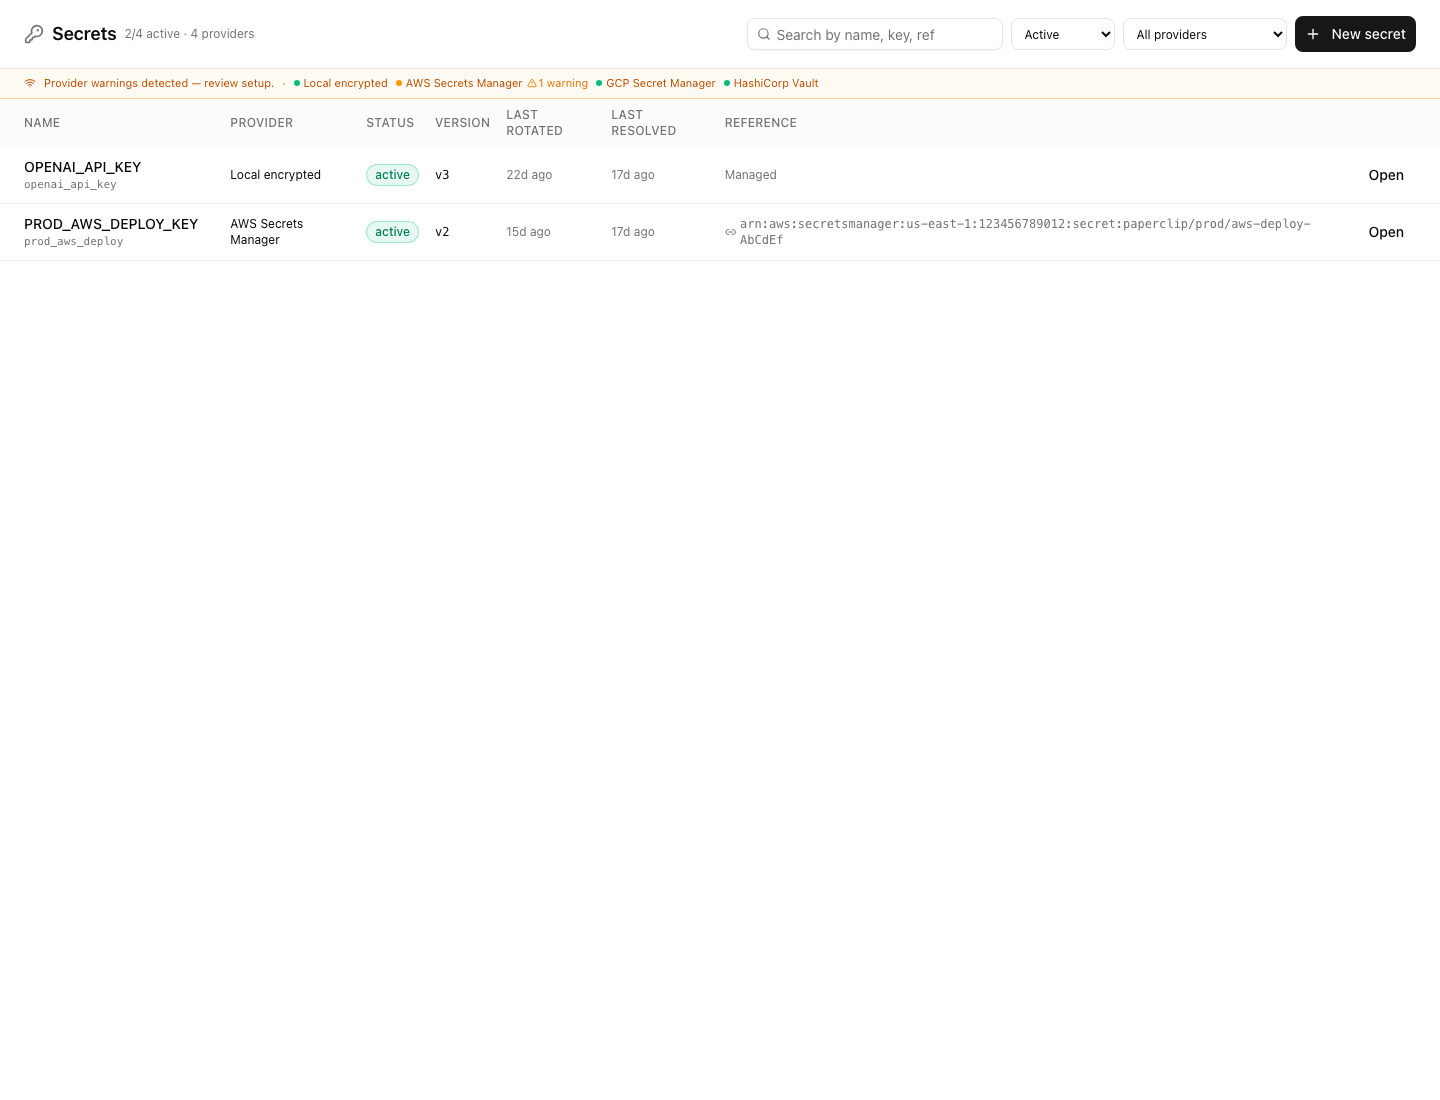 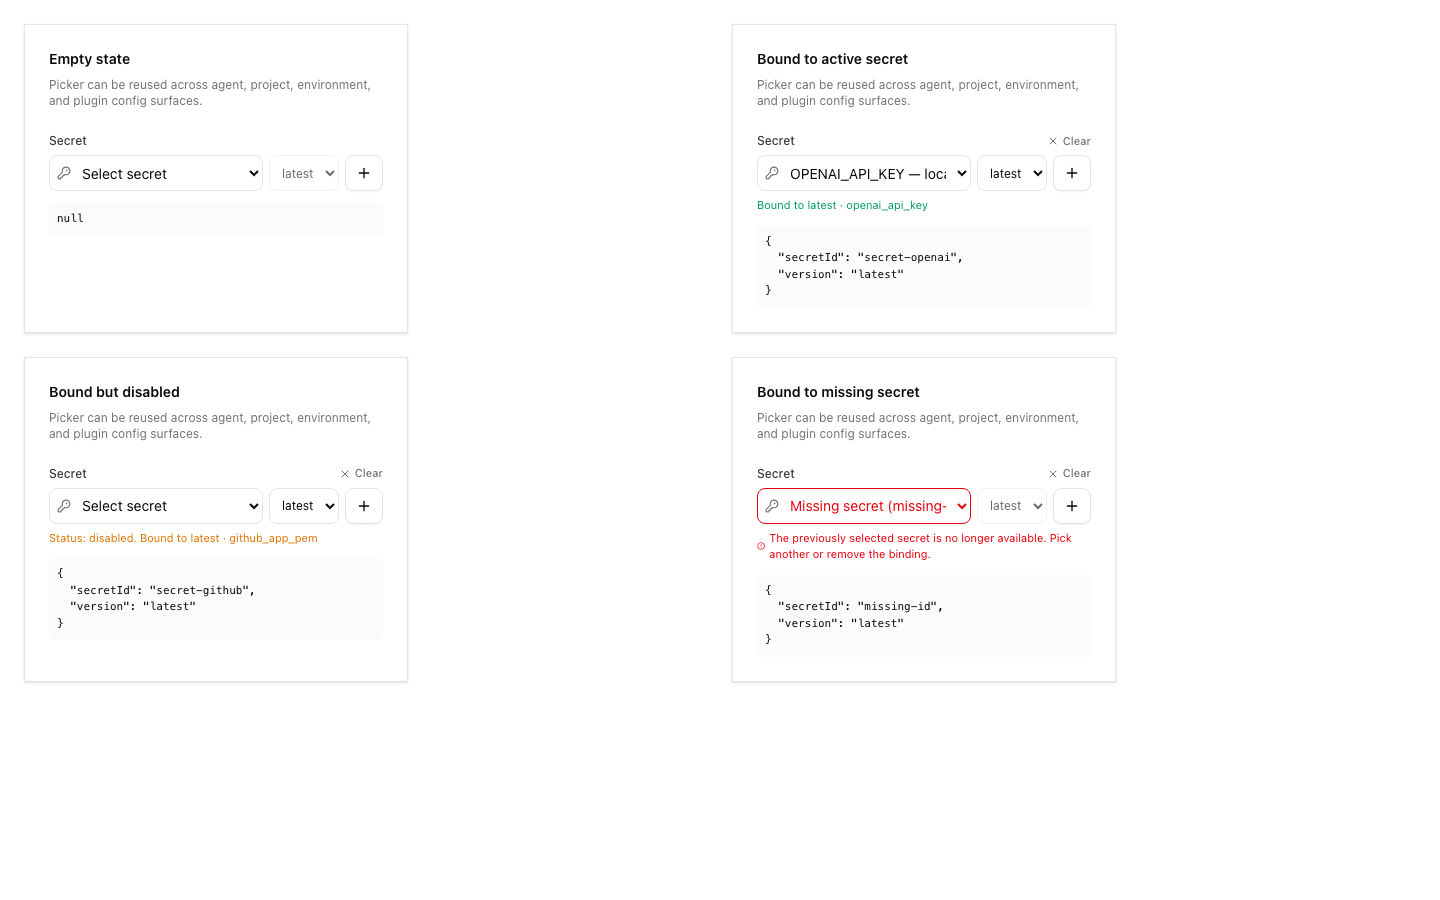 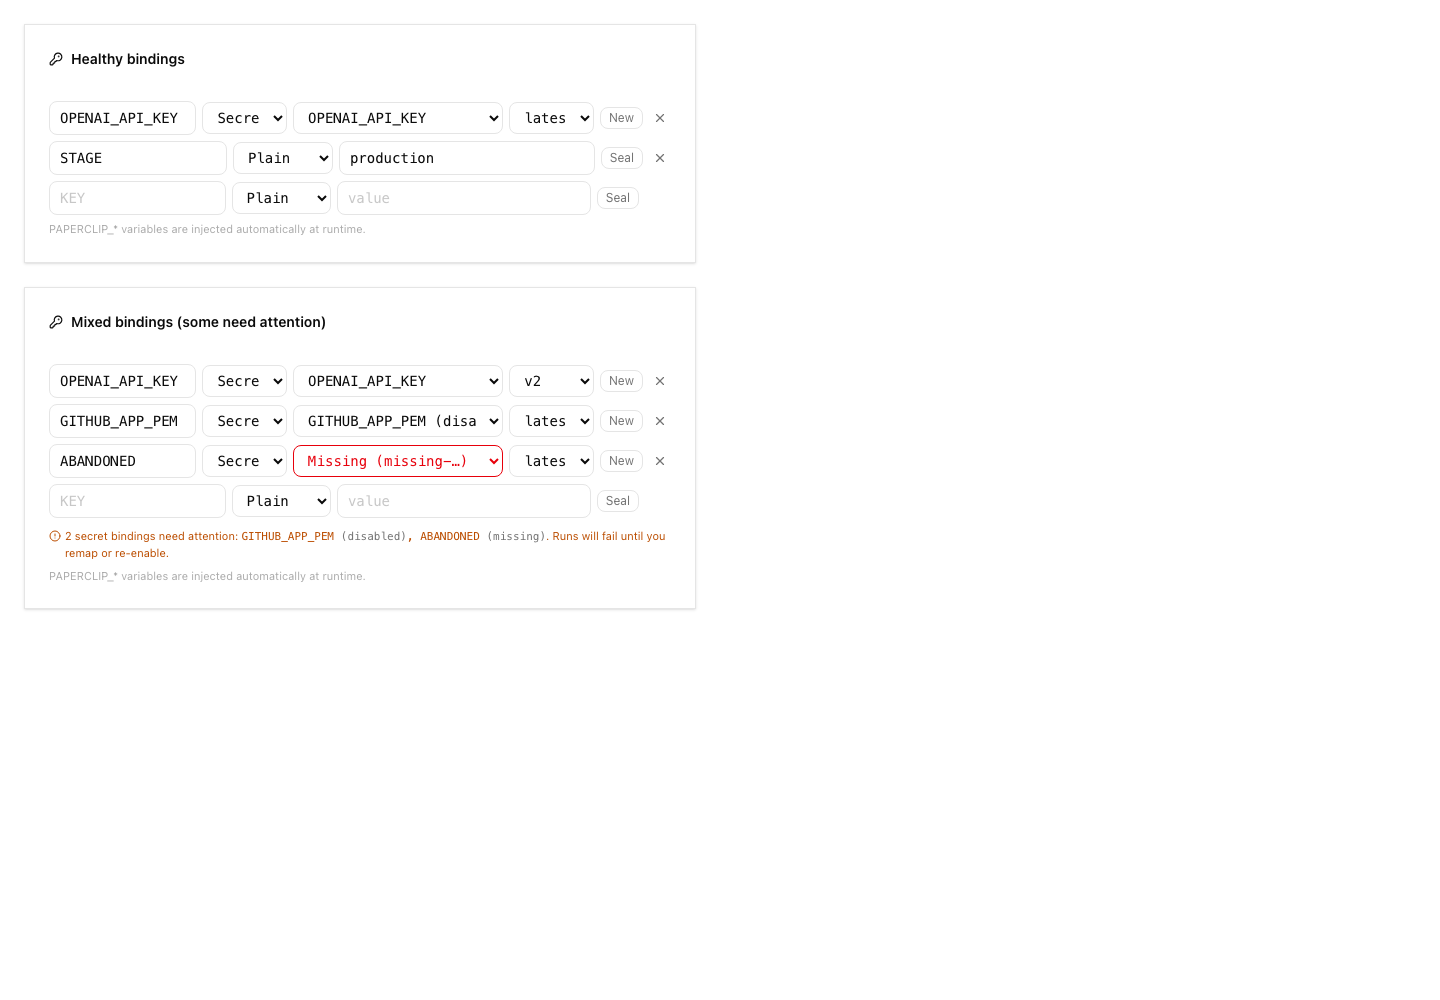 ## Risks - Migration risk: this adds new secret provider tables and extends existing secret rows. The migrations were checked for monotonic ordering and idempotent guards, but reviewers should still inspect upgrade behavior carefully. - Provider risk: AWS support uses direct SigV4 requests. Automated tests cover signing, request timeouts, vault-config selection, namespace guardrails, pending-version archival, sanitized provider errors, and service-level cleanup paths. A real-vault AWS smoke test remains deployment validation for an operator with AWS credentials rather than an unverified merge blocker in this local branch. - UI risk: the Secrets page and import dialog are large new surfaces; screenshots are included above for reviewer inspection. - Verification risk: the full local stable test command hit parallel-load timing failures, although the exact failed files passed when rerun directly. - Operational risk: remote import intentionally avoids plaintext reads; operators must understand that imported external references resolve at runtime and may fail if AWS permissions change. > For core feature work, check [`ROADMAP.md`](ROADMAP.md) first and discuss it in `#dev` before opening the PR. Feature PRs that overlap with planned core work may need to be redirected — check the roadmap first. See `CONTRIBUTING.md`. ## Model Used - OpenAI Codex, GPT-5 coding agent with local shell/tool use in the Paperclip worktree. Exact context-window size was not exposed by the runtime. ## Checklist - [x] I have included a thinking path that traces from project context to this change - [x] I have specified the model used (with version and capability details) - [x] I have checked ROADMAP.md and confirmed this PR does not duplicate planned core work - [ ] I have run tests locally and they pass - [x] I have added or updated tests where applicable - [x] If this change affects the UI, I have included before/after screenshots - [x] I have updated relevant documentation to reflect my changes - [x] I have considered and documented any risks above - [x] I will address all Greptile and reviewer comments before requesting merge --------- Co-authored-by: Paperclip <noreply@paperclip.ing> Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com> |
||
|
DottaandClaude Opus 4.6
|
f60c1001ec |
refactor: rename packages to @paperclipai and CLI binary to paperclipai
Rename all workspace packages from @paperclip/* to @paperclipai/* and the CLI binary from `paperclip` to `paperclipai` in preparation for npm publishing. Bump CLI version to 0.1.0 and add package metadata (description, keywords, license, repository, files). Update all imports, documentation, user-facing messages, and tests accordingly. Co-Authored-By: Claude Opus 4.6 <noreply@anthropic.com> |
||
|
Forgotten
|
8f3fc077fa | feat(cli): add client commands and home-based local runtime defaults | ||
|
ForgottenandClaude Opus 4.6
|
f1b558dcfb |
CLI: add secrets configuration, doctor check, and path resolver extraction
Add secrets section to onboard, configure, and doctor commands. Doctor validates local encrypted provider key file and can auto-repair missing keys. Extract shared path resolution into path-resolver module used by database and log checks. Show secrets env vars in `paperclip env`. Co-Authored-By: Claude Opus 4.6 <noreply@anthropic.com> |


