mirror of
https://github.com/paperclipai/paperclip.git
synced 2026-11-12 14:19:00 +01:00
42bc238aa5a1208cabecba76773e0500fcd33959
2
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 phant0umandClaude Opus 5.5 |
c4171af889 |
fix(cli): skip POSIX key file mode check in doctor on Windows (#14308)
## Thinking Path > - Paperclip is the open source app people use to manage AI agents for work > - `paperclipai doctor` checks the local install, including the local encrypted secrets key file > - The check reads the POSIX permission bits of the key file and warns when group or others can read it > - On Windows, `fs.statSync().mode` is always `0o666` for a writable file, and `chmod` cannot restrict it > - So on Windows the check always warns, and the suggested `chmod 600` has no effect > - The server secret provider health check has the same check and the same false positive > - This pull request skips the POSIX permission-bit check on `win32` in both places > - The benefit is that `doctor` and the secret provider health endpoints on Windows no longer show a permanent false-positive warning ## Linked Issues or Issue Description Fixes #14255 ## What Changed - `cli/src/checks/secrets-check.ts`: skip the key file permission-bit check when `process.platform === "win32"`. Linux and macOS behavior does not change. - `cli/src/__tests__/secrets.test.ts`: add two tests. One test mocks `process.platform` as `win32` and expects `pass` for a `0o666` key file. One test pins the POSIX behavior: a `0o644` key file still gives `warn` (skipped on Windows runners). - `server/src/secrets/local-encrypted-provider.ts`: the same `win32` skip in the local encrypted provider health check. This check feeds `GET /api/companies/{id}/secret-providers/health`, `POST /api/secret-provider-configs/{id}/health`, and the `validateConfig` warnings. - `server/src/__tests__/secret-provider-registry.test.ts`: add a `win32` test that expects status `ok` with no warnings for a `0o666` key file. Mark the existing `0o644` warning test `skipIf(win32)`. ## Verification - `cd cli && npx vitest run src/__tests__/secrets.test.ts`: 10 of 10 tests pass on macOS (Node 22.22.3). - Red before the fix: with the fix reverted, 1 failed and 9 passed. The new Windows test fails with `expected 'warn' to be 'pass'`. - `cd server && npx vitest run src/__tests__/secret-provider-registry.test.ts`: 3 of 3 tests pass. Red before the fix: the new `win32` test failed 2 times with status `warn`. - Full CLI suite (`cd cli && npx vitest run`): the same 28 tests in `doctor`, `install-command`, `update-command`, and `worktree` fail on `master` without this change and with it. My local checkout has no workspace builds, because I installed with `--ignore-scripts`. This change adds 2 passing tests and no new failures. - `cd cli && npx tsc --noEmit`: 233 errors on `master` and 233 with this change. All errors come from unbuilt workspace packages. No error is in `cli/src`. - I did not run the check on a real Windows machine. The Windows test mocks `process.platform`. ## Risks - Low risk. The change only removes a warning on Windows. On Windows the old check always fired, so it gave no signal. - The repo already skips the same kind of check on `win32`: `server/src/services/decision-signing.ts` returns early in `assertOwnedByCurrentUser` and `enforceKeyFilePermissions` for its key file. - On Windows, `doctor` no longer checks key file access at all. NTFS ACLs control access there, and the old check could not read them. An ACL check is out of scope for this fix. ## Model Used - Claude Opus 5.5 (`claude-opus-5-5`, Anthropic), in Claude Code with tool use (shell, file edit). It reproduced the bug with a failing test, wrote the fix, and drafted this description. A human reviewed the change. ## Checklist - [x] I have included a thinking path that traces from project context to this change - [x] I have specified the model used (with version and capability details) - [x] I have checked ROADMAP.md and confirmed this PR does not duplicate planned core work - [x] I have searched GitHub for duplicate or related PRs and linked them above - [x] I have either (a) linked existing issues with `Fixes: #` / `Closes #` / `Refs #` OR (b) described the issue in-PR following the relevant issue template - [x] I have not referenced internal/instance-local Paperclip issues or links (only public GitHub `#NNN` / `github.com/paperclipai/paperclip` URLs) - [x] My branch name describes the change (e.g. `docs/...`, `fix/...`) and contains no internal Paperclip ticket id or instance-derived details - [x] I have run tests locally and they pass - [x] I have added or updated tests where applicable - [ ] I have updated relevant documentation to reflect my changes (no documentation describes this warning) - [x] I have considered and documented any risks above - [x] All Paperclip CI gates are green - [x] Greptile is 5/5 with no open P2s, recommendations, or follow-ups - [x] I will address all Greptile and reviewer comments before requesting merge --------- Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com> |
||
|
|
778e775c35 |
Add secrets provider vaults and remote import (#5429)
## Thinking Path > - Paperclip orchestrates AI-agent companies and needs secrets handling to work across local development, hosted operators, and governed agent execution. > - The affected subsystem is the company-scoped secrets control plane: database schema, server services/routes, CLI workflows, and the Secrets settings UI. > - The gap was that secrets were local-only and operators could not manage provider vaults or import existing remote references without exposing plaintext. > - This branch adds provider vault configuration plus an AWS Secrets Manager remote-import path while preserving company boundaries, binding context, and audit trails. > - I kept the PR to a single branch PR, removed unrelated lockfile/package drift, rebased the full branch onto the current `public-gh/master`, and addressed fresh Greptile findings. > - The benefit is a reviewable implementation of provider-backed secrets with focused tests covering provider selection, import conflicts, deleted secret reuse, rotation guards, and AWS signing behavior. ## What Changed - Added provider vault support for company secrets, including provider config storage, default vault handling, health checks, binding usage, access events, and remote import preview/commit. - Added an AWS Secrets Manager provider using SigV4 request signing, bounded request timeouts, namespace guardrails, cached runtime credential resolution, and external-reference linking without plaintext reads. - Added Secrets UI surfaces for vault management and remote import, plus CLI/API documentation for setup and operations. - Stabilized routine webhook secret binding paths and SSH environment-driver fixture bindings discovered during verification. - Addressed Greptile and CI findings: no lockfile/package drift, monotonic migration metadata, disabled-vault default races, soft-deleted secret hiding/recreate behavior, remove behavior with disabled vaults, soft-deleted external-reference re-import, non-active rotation guards, managed-secret soft deletion through PATCH, and per-call AWS SDK credential client churn. - Rebased this branch onto `public-gh/master` at `0e1a5828` and force-pushed with lease to keep this as the single PR for the branch. ## Verification - `git fetch public-gh master` - `git rebase public-gh/master` - `git diff --name-only public-gh/master...HEAD | grep '^pnpm-lock\.yaml$' || true` confirmed `pnpm-lock.yaml` is not in the PR diff. - Confirmed migration ordering: master ends at `0081_optimal_dormammu`; this PR adds `0082_dry_vision` and `0083_company_secret_provider_configs`. - Inspected migrations for repeat safety: new tables/indexes use `IF NOT EXISTS`; foreign keys are guarded by `DO $$ ... IF NOT EXISTS`; column additions use `ADD COLUMN IF NOT EXISTS`. - `pnpm -r typecheck` passed before the Greptile follow-up commits. - `pnpm test:run` ran the full stable Vitest path before the Greptile follow-up commits; it completed with 3 timing-related failures under parallel load: `codex-local-execute.test.ts`, `cursor-local-execute.test.ts`, and `environment-service.test.ts`. - `pnpm --filter @paperclipai/server exec vitest run src/__tests__/codex-local-execute.test.ts src/__tests__/cursor-local-execute.test.ts src/__tests__/environment-service.test.ts` passed on targeted rerun (`24/24`). - `pnpm build` passed before the Greptile follow-up commits. Vite reported existing chunk-size/dynamic-import warnings. - After Greptile follow-up commits: `pnpm --filter @paperclipai/server exec vitest run src/__tests__/secrets-service.test.ts` passed (`26/26`). - After Greptile follow-up commits: `pnpm --filter @paperclipai/server exec vitest run src/__tests__/aws-secrets-manager-provider.test.ts src/__tests__/secrets-service.test.ts` passed (`39/39`). - After Greptile follow-up commits: `pnpm --filter @paperclipai/server typecheck` passed. - Captured Storybook screenshots from `ui/storybook-static` for visual review. - Latest PR checks on `5ca3a5cf`: `policy`, serialized server suites 1/4-4/4, `Canary Dry Run`, `e2e`, `security/snyk`, and `Greptile Review` pass; aggregate `verify` is still registering the completed child checks. - Greptile review loop continued through the latest requested pass; all Greptile review threads are resolved and the latest `Greptile Review` check on `5ca3a5cf` passed with 0 comments added. ## Screenshots Before: the provider-vault and remote-import surfaces did not exist on `master`; these are after-state screenshots from the Storybook fixtures. 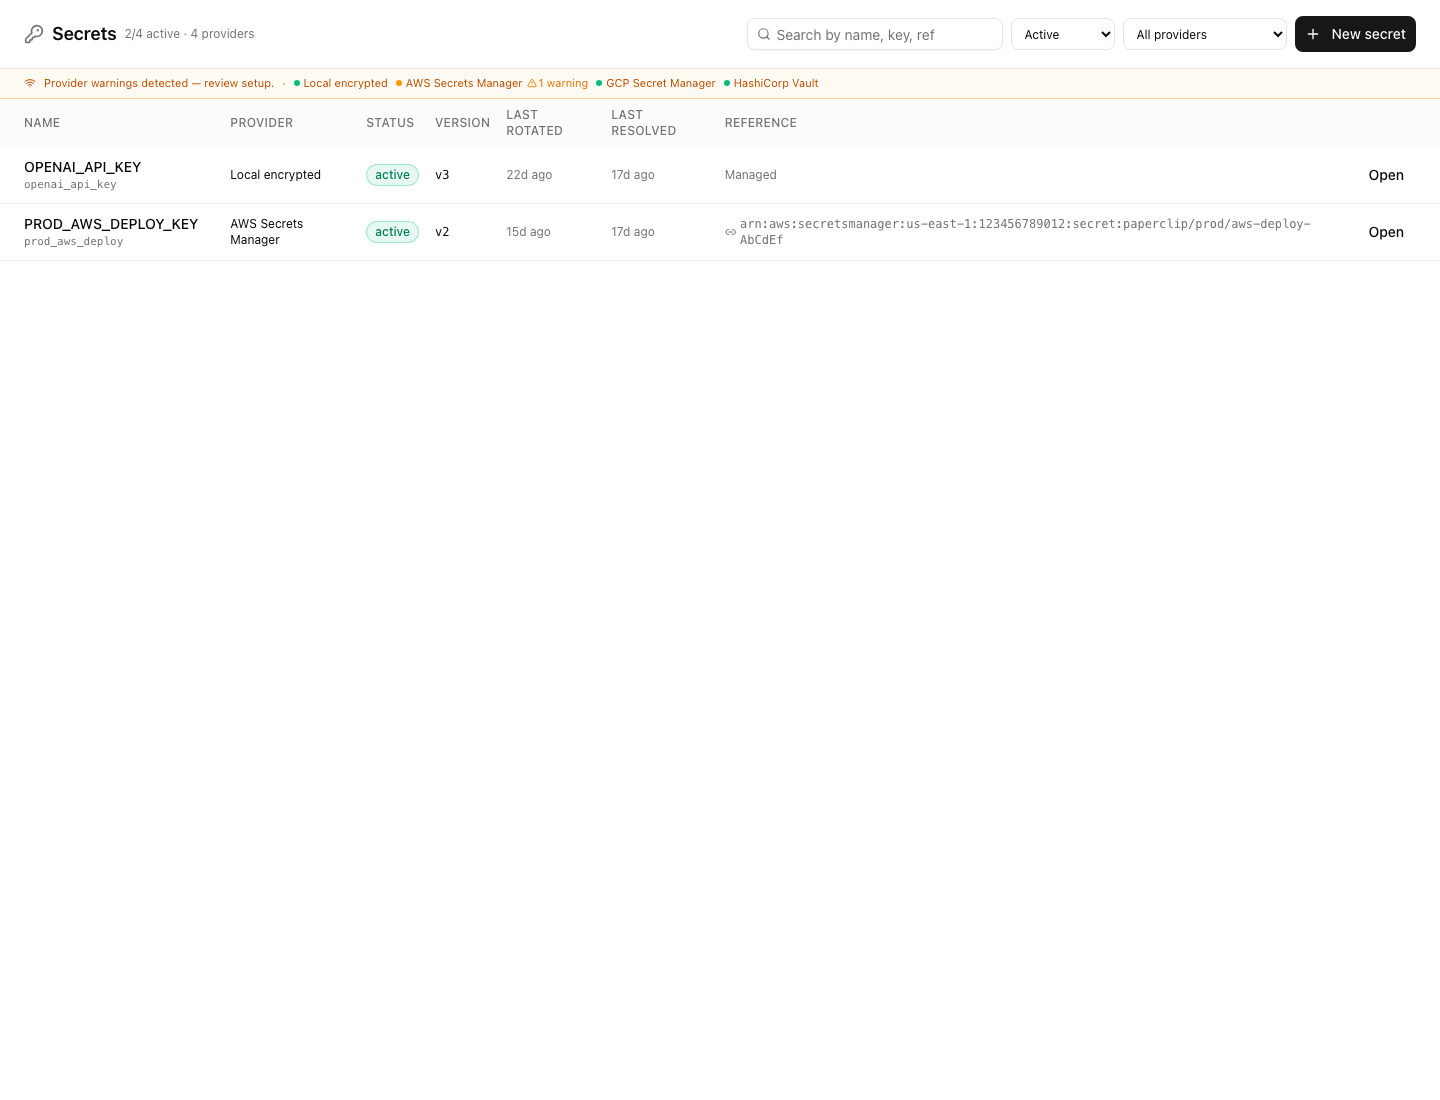 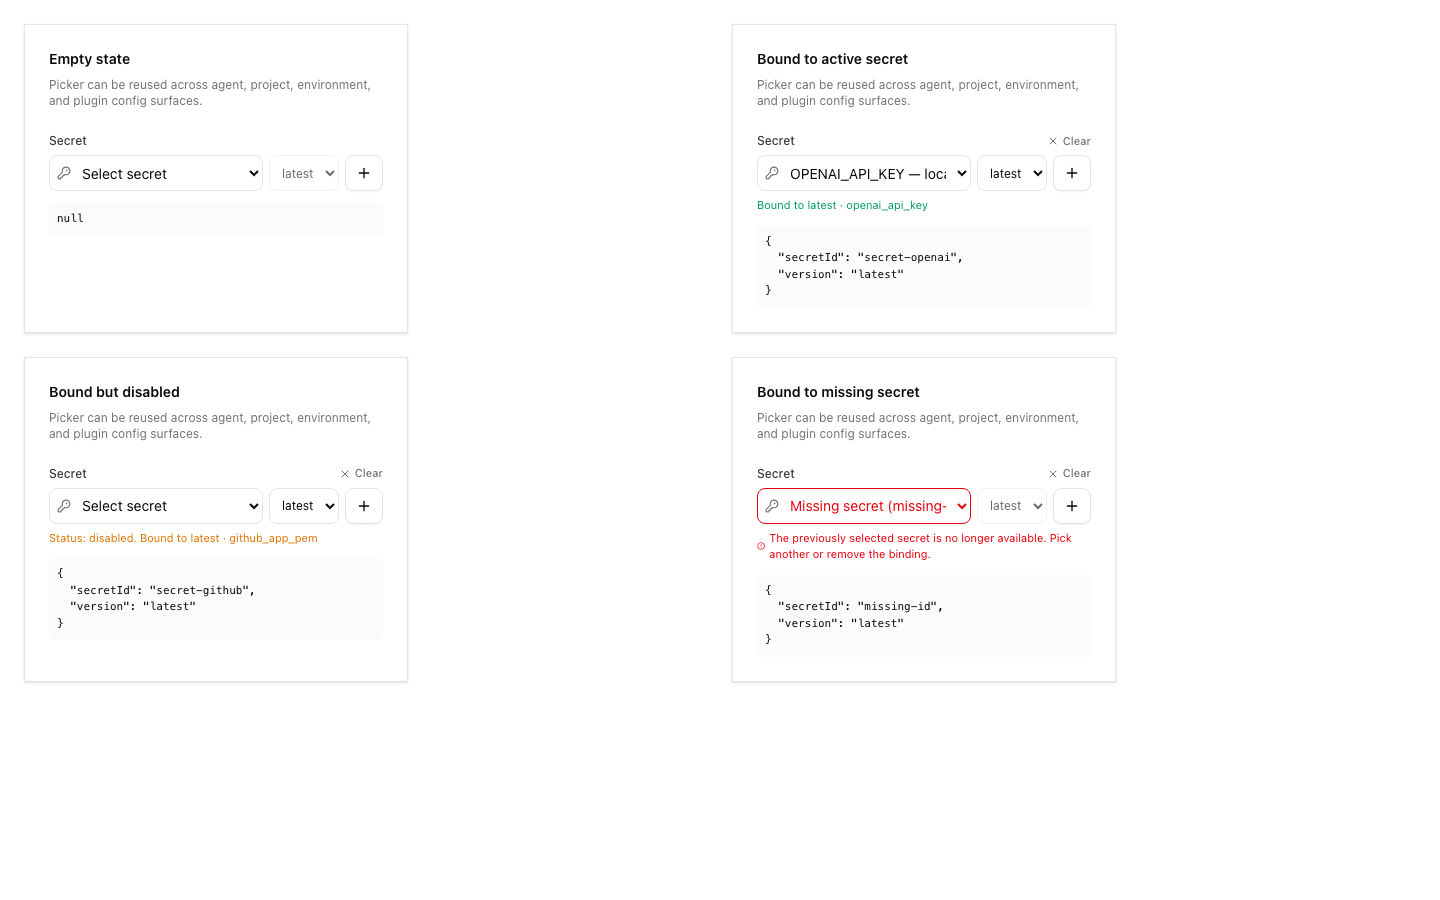 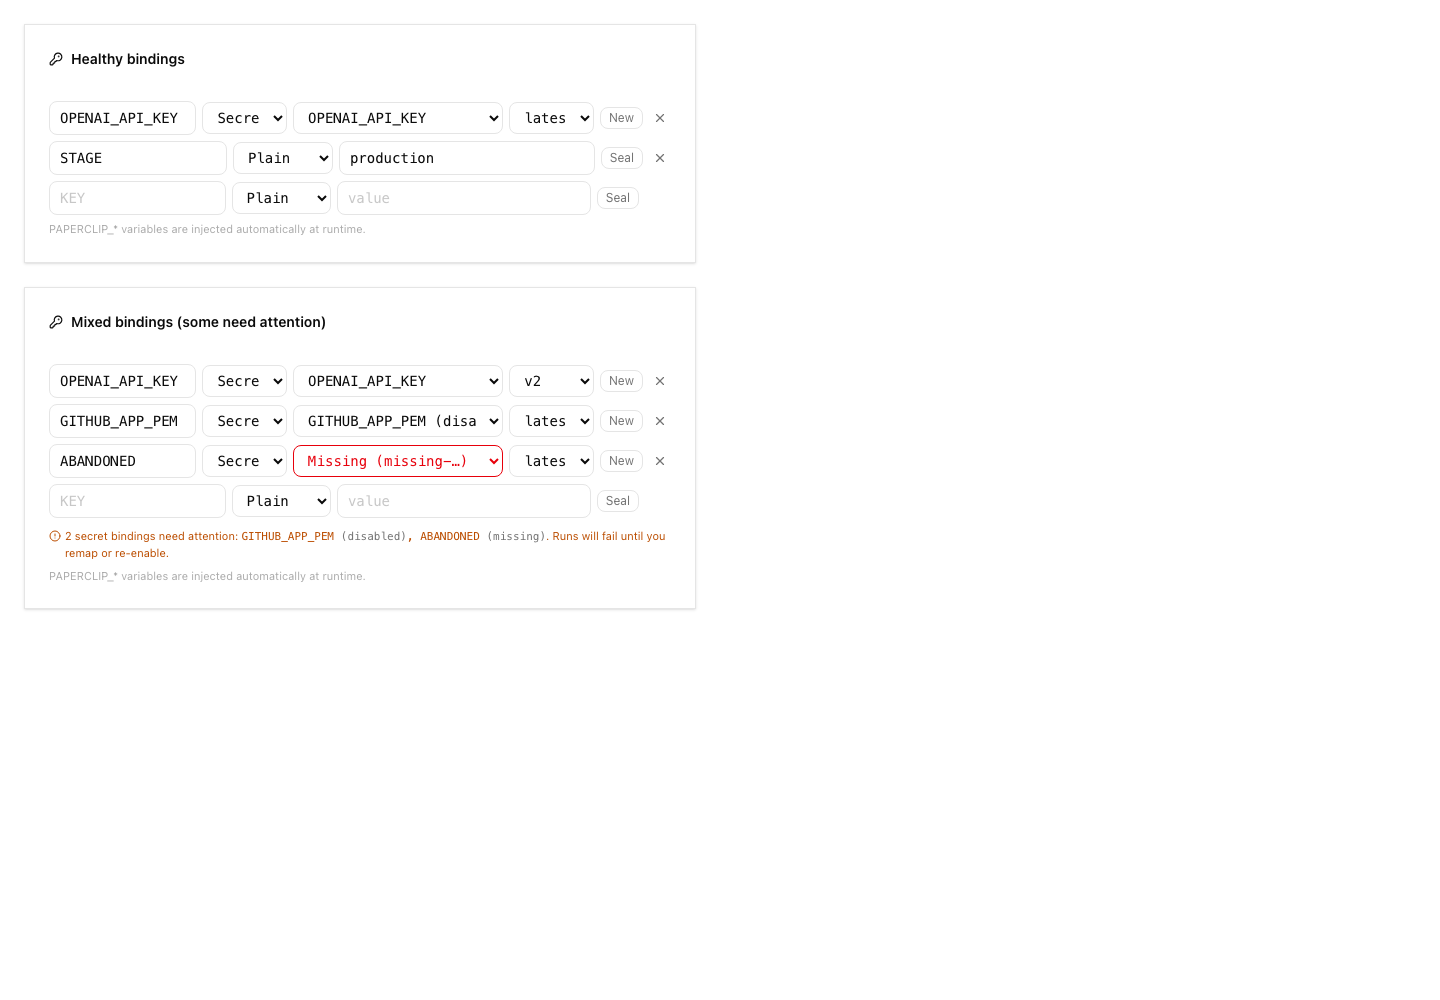 ## Risks - Migration risk: this adds new secret provider tables and extends existing secret rows. The migrations were checked for monotonic ordering and idempotent guards, but reviewers should still inspect upgrade behavior carefully. - Provider risk: AWS support uses direct SigV4 requests. Automated tests cover signing, request timeouts, vault-config selection, namespace guardrails, pending-version archival, sanitized provider errors, and service-level cleanup paths. A real-vault AWS smoke test remains deployment validation for an operator with AWS credentials rather than an unverified merge blocker in this local branch. - UI risk: the Secrets page and import dialog are large new surfaces; screenshots are included above for reviewer inspection. - Verification risk: the full local stable test command hit parallel-load timing failures, although the exact failed files passed when rerun directly. - Operational risk: remote import intentionally avoids plaintext reads; operators must understand that imported external references resolve at runtime and may fail if AWS permissions change. > For core feature work, check [`ROADMAP.md`](ROADMAP.md) first and discuss it in `#dev` before opening the PR. Feature PRs that overlap with planned core work may need to be redirected — check the roadmap first. See `CONTRIBUTING.md`. ## Model Used - OpenAI Codex, GPT-5 coding agent with local shell/tool use in the Paperclip worktree. Exact context-window size was not exposed by the runtime. ## Checklist - [x] I have included a thinking path that traces from project context to this change - [x] I have specified the model used (with version and capability details) - [x] I have checked ROADMAP.md and confirmed this PR does not duplicate planned core work - [ ] I have run tests locally and they pass - [x] I have added or updated tests where applicable - [x] If this change affects the UI, I have included before/after screenshots - [x] I have updated relevant documentation to reflect my changes - [x] I have considered and documented any risks above - [x] I will address all Greptile and reviewer comments before requesting merge --------- Co-authored-by: Paperclip <noreply@paperclip.ing> Co-authored-by: Claude Sonnet 4.6 <noreply@anthropic.com> |


